
A complete security layer for AI. Interpretable defence.
Every AI. Every interaction. Every decision. Trusted. I-THAM wraps your AI in one interpretable security layer, with five product areas that work before deployment, at runtime and after every decision.
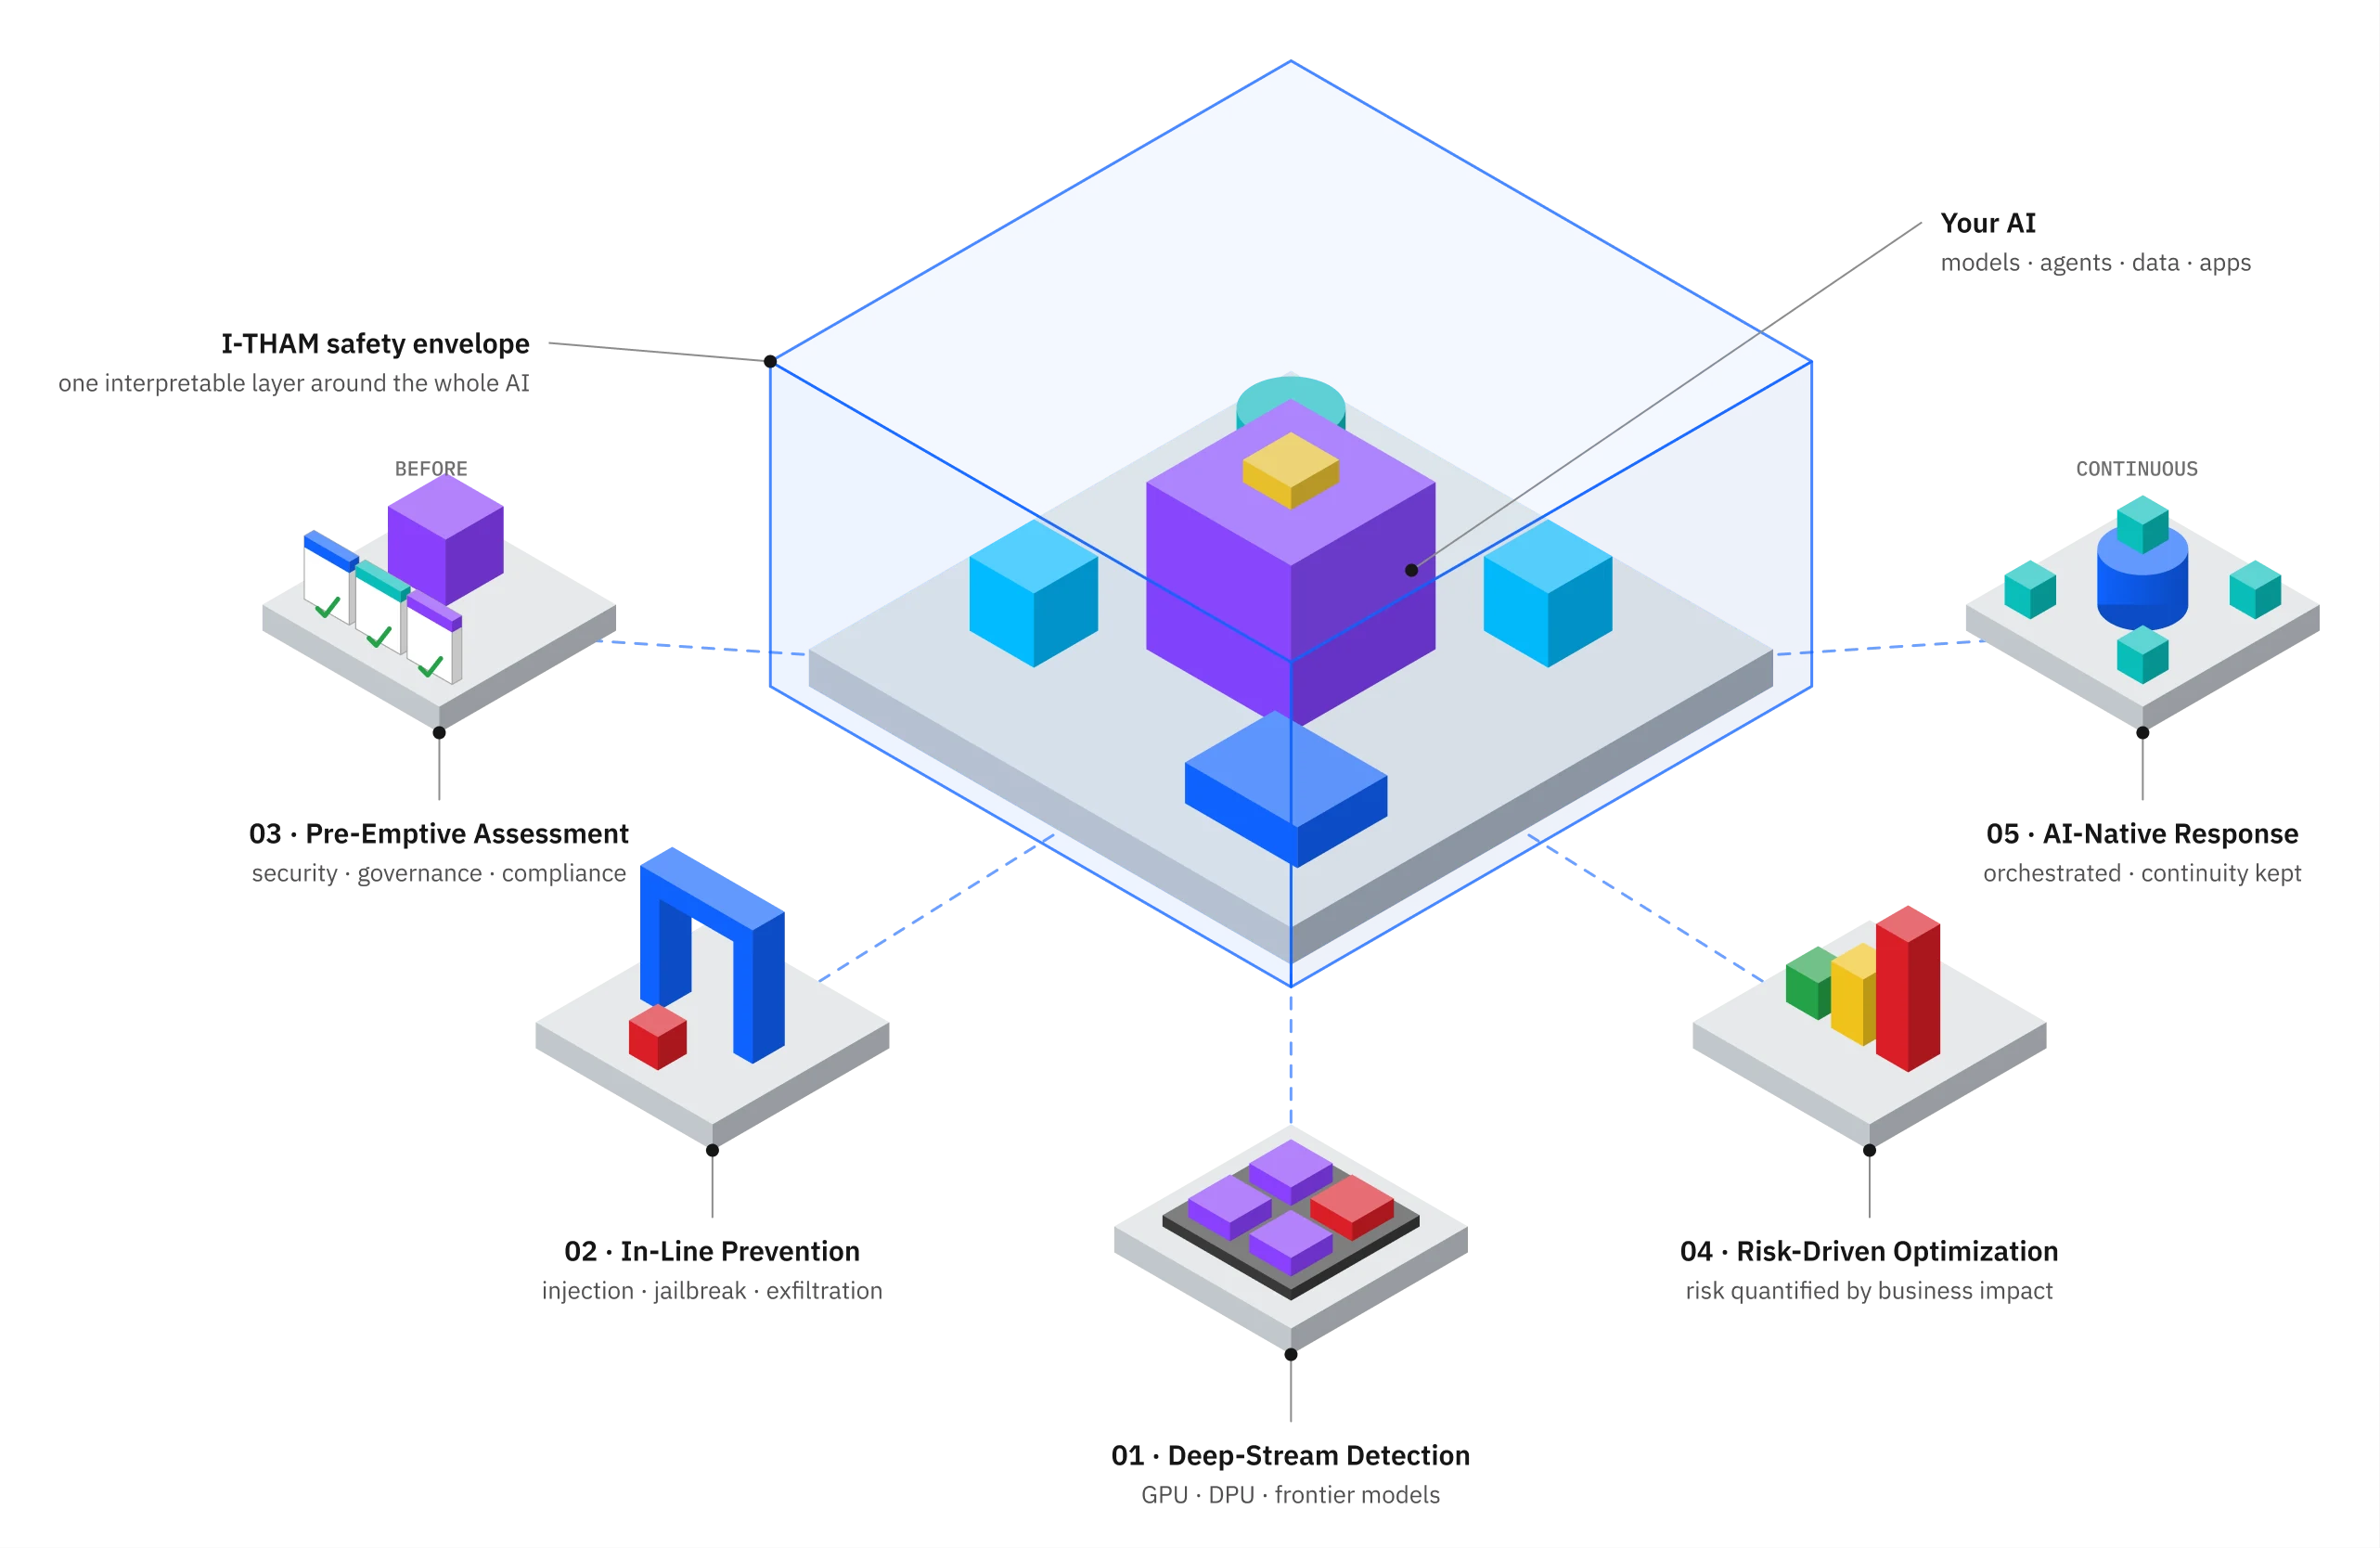
- Deep-Stream DetectionNovel attack surface across models, agents and AI internals.
- In-Line PreventionInjection, jailbreaks and exfiltration stopped as they happen.
- Pre-Emptive AssessmentSecurity, governance and compliance before production.
- Risk-Driven OptimizationRemediation focused where it matters most.
- AI-Native Response OrchestratorReal-time response with business continuity.
Deep-Stream Detection
Proprietary Deep-Stream inspection for novel attack surface across models, agents and AI internals, including GPU, DPU and frontier models. It also sees attempts to steal or tamper with your models.
Questions it helps you answer
- Is anything abnormal happening inside our models, not only in their outputs?
- Are our agents being steered somewhere they should not go?
- Can we see attacks that never touch the prompt?
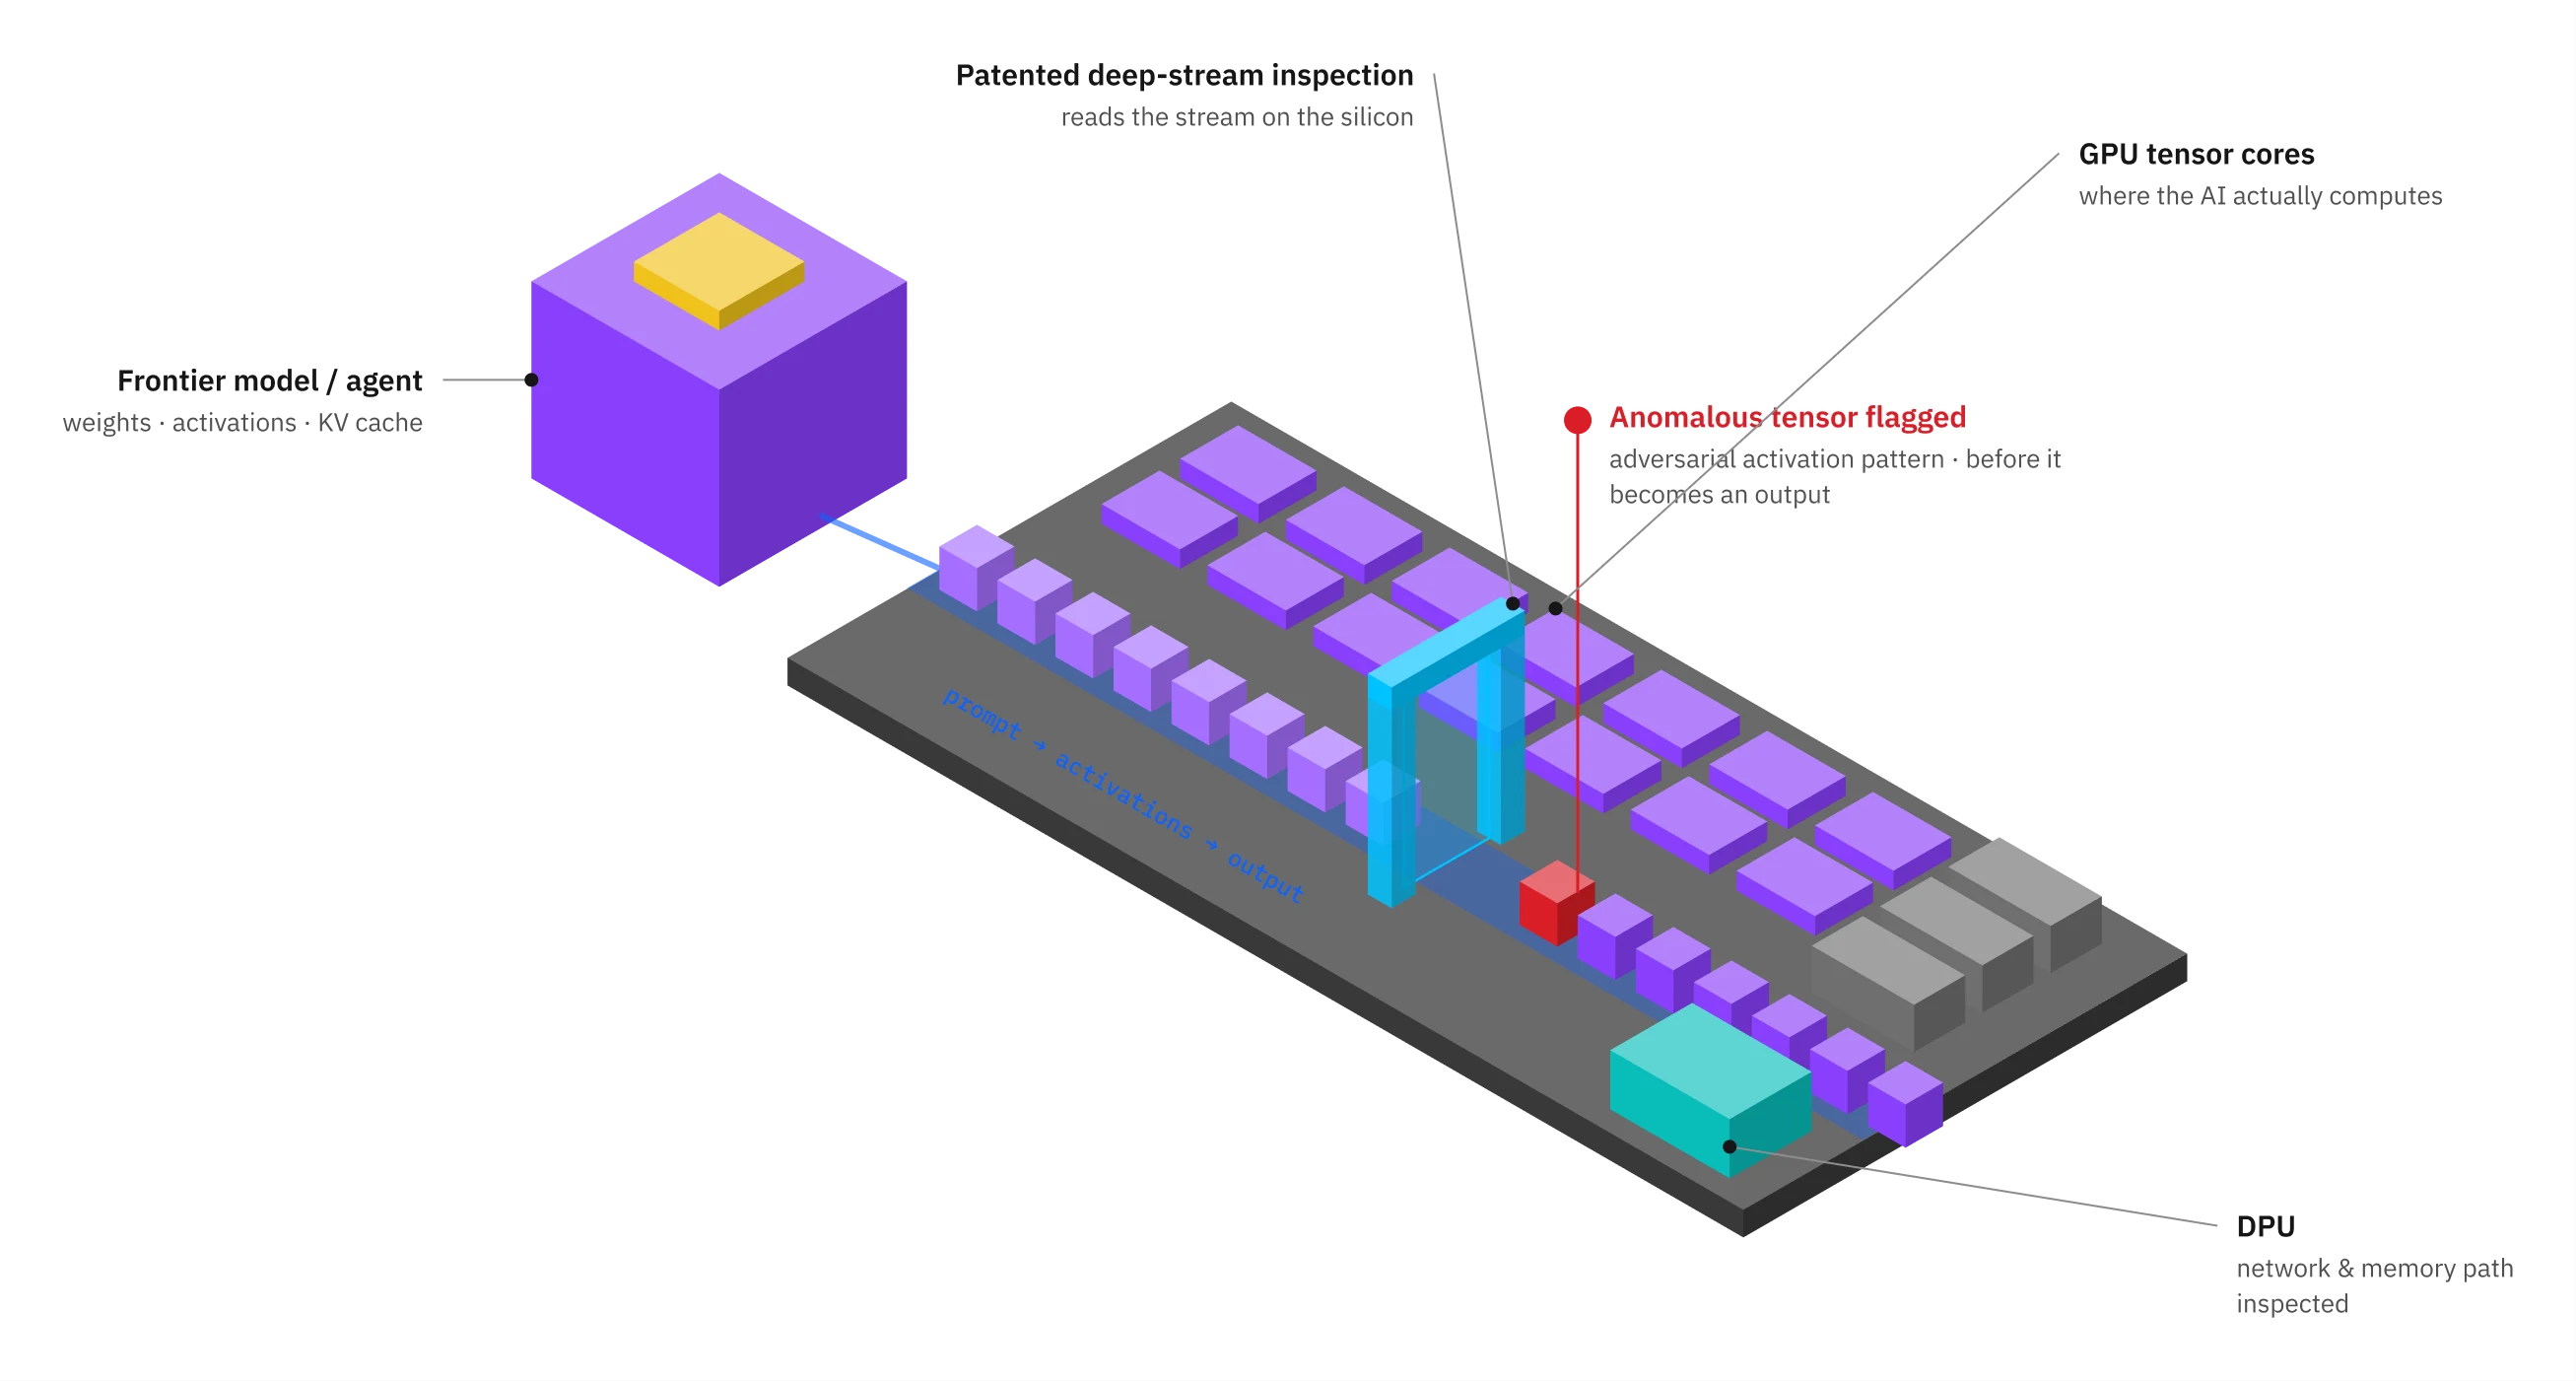
- Models and agentsThe AI you run, from frontier models to your own agents.
- Deep-Stream inspectionProprietary inspection of the stream where AI actually computes.
- Anomaly flaggedCaught before it becomes an output.
- GPU and DPUCoverage extends down to the silicon.
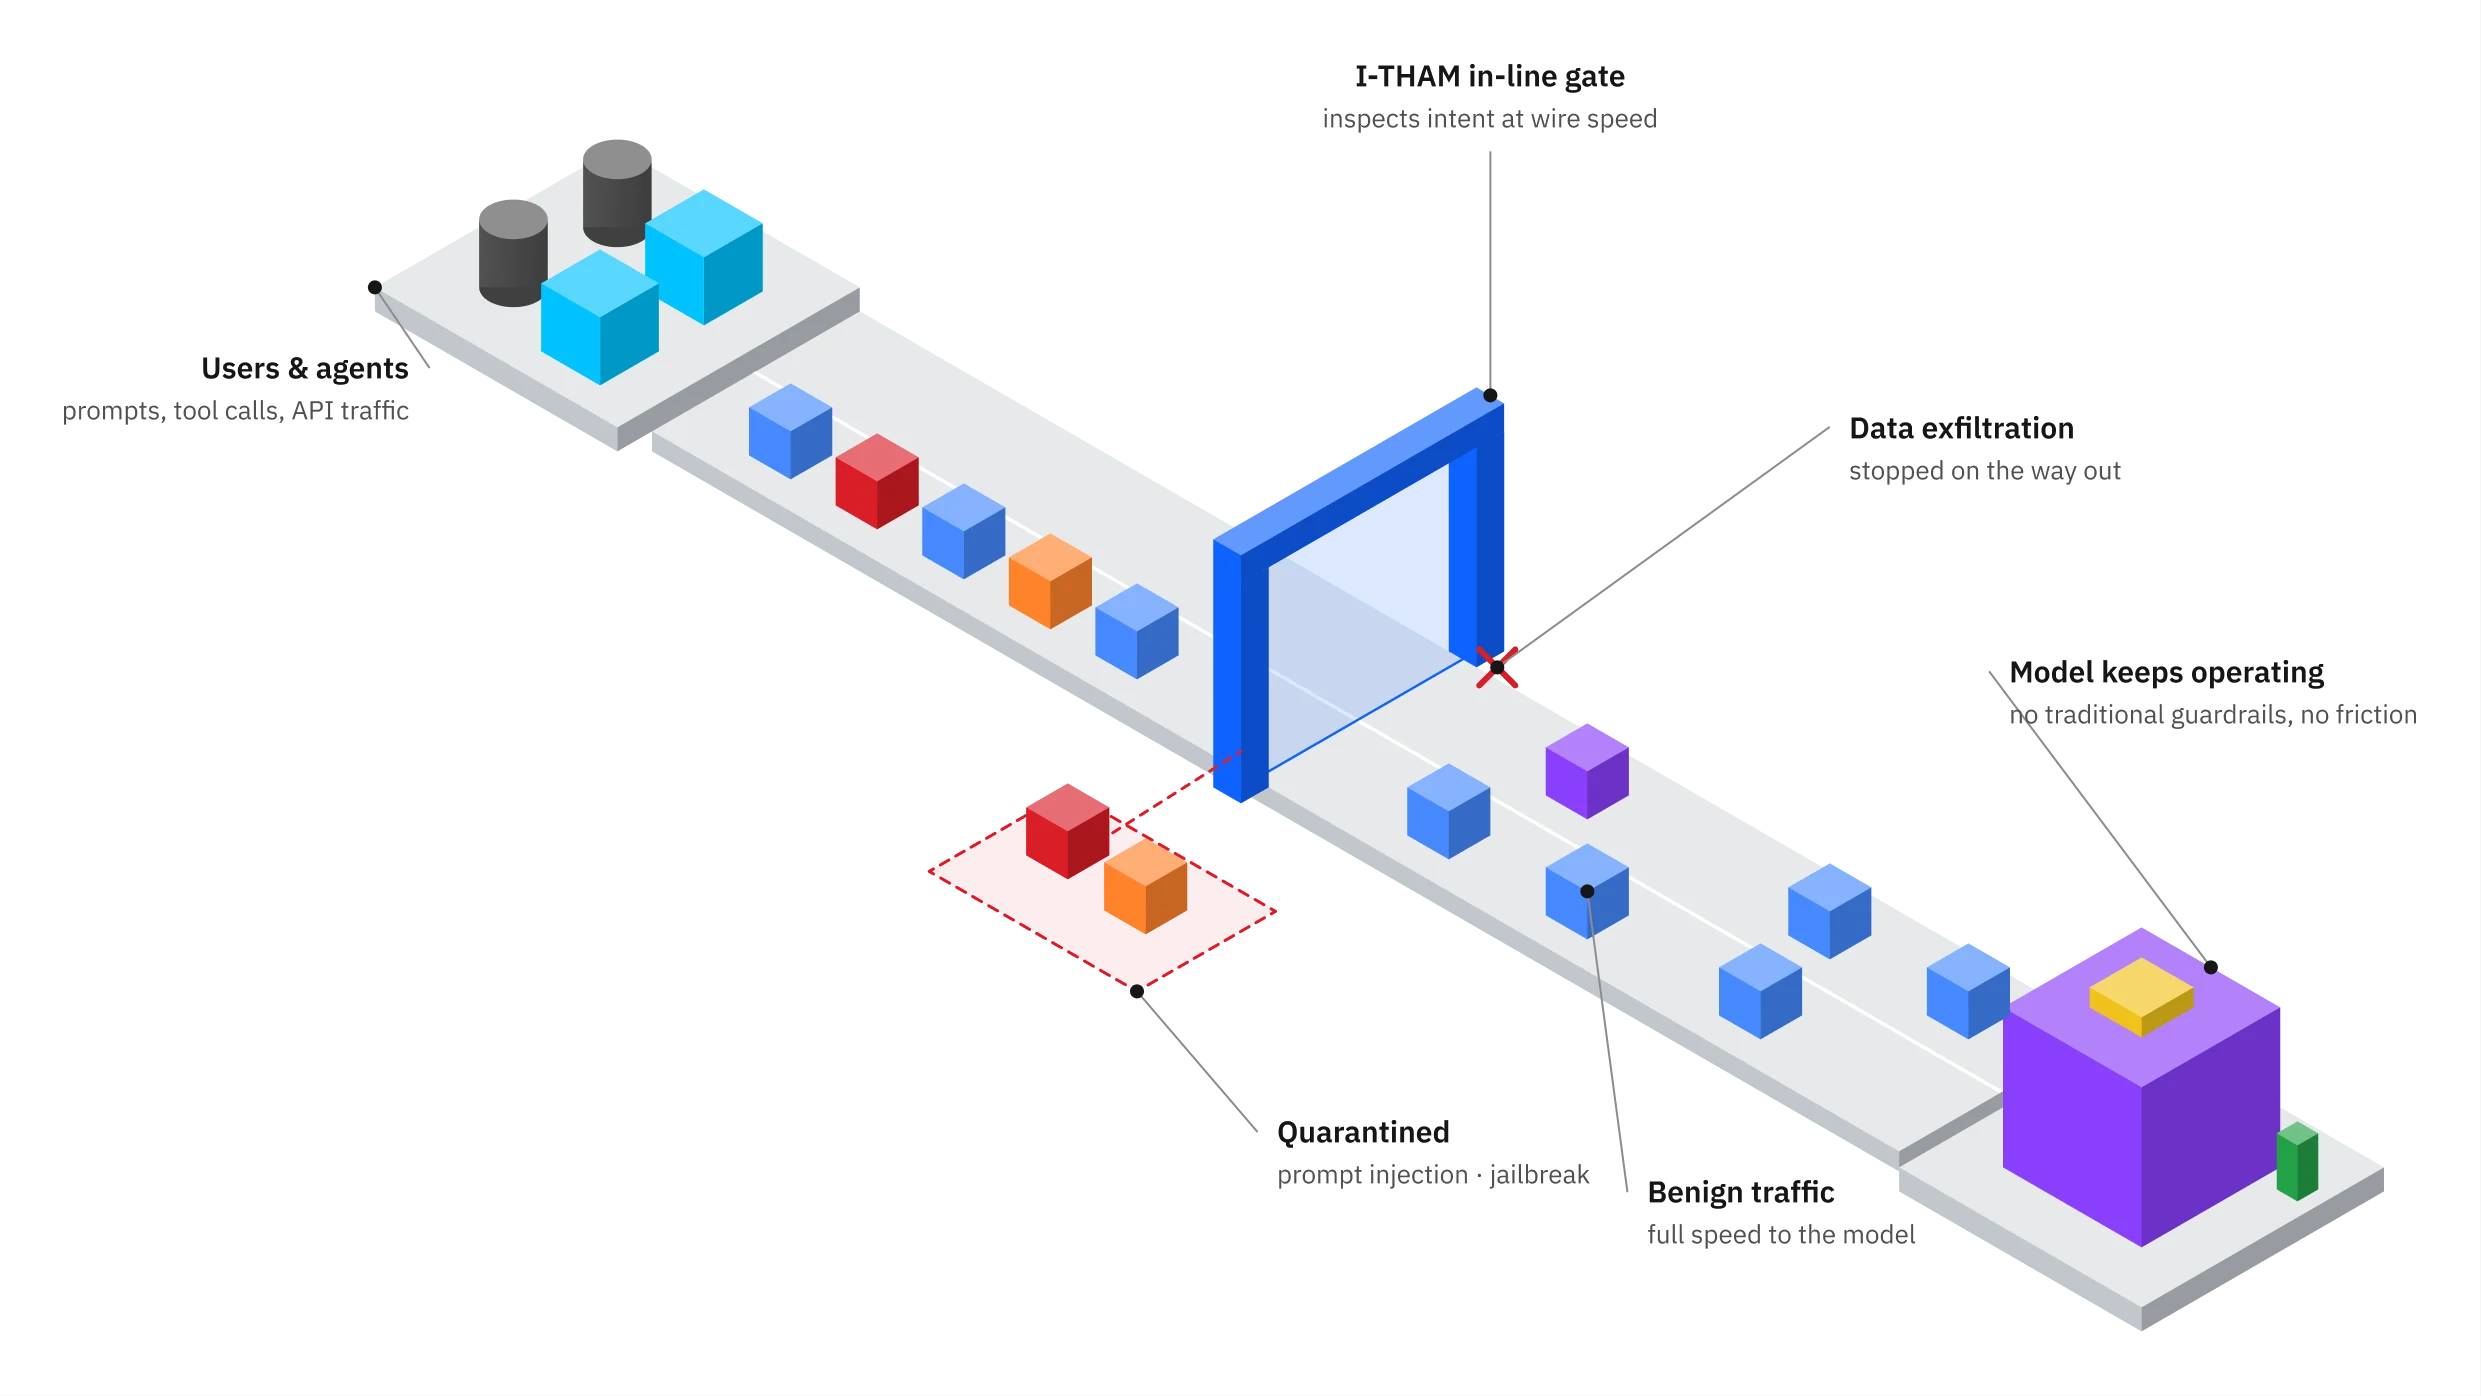
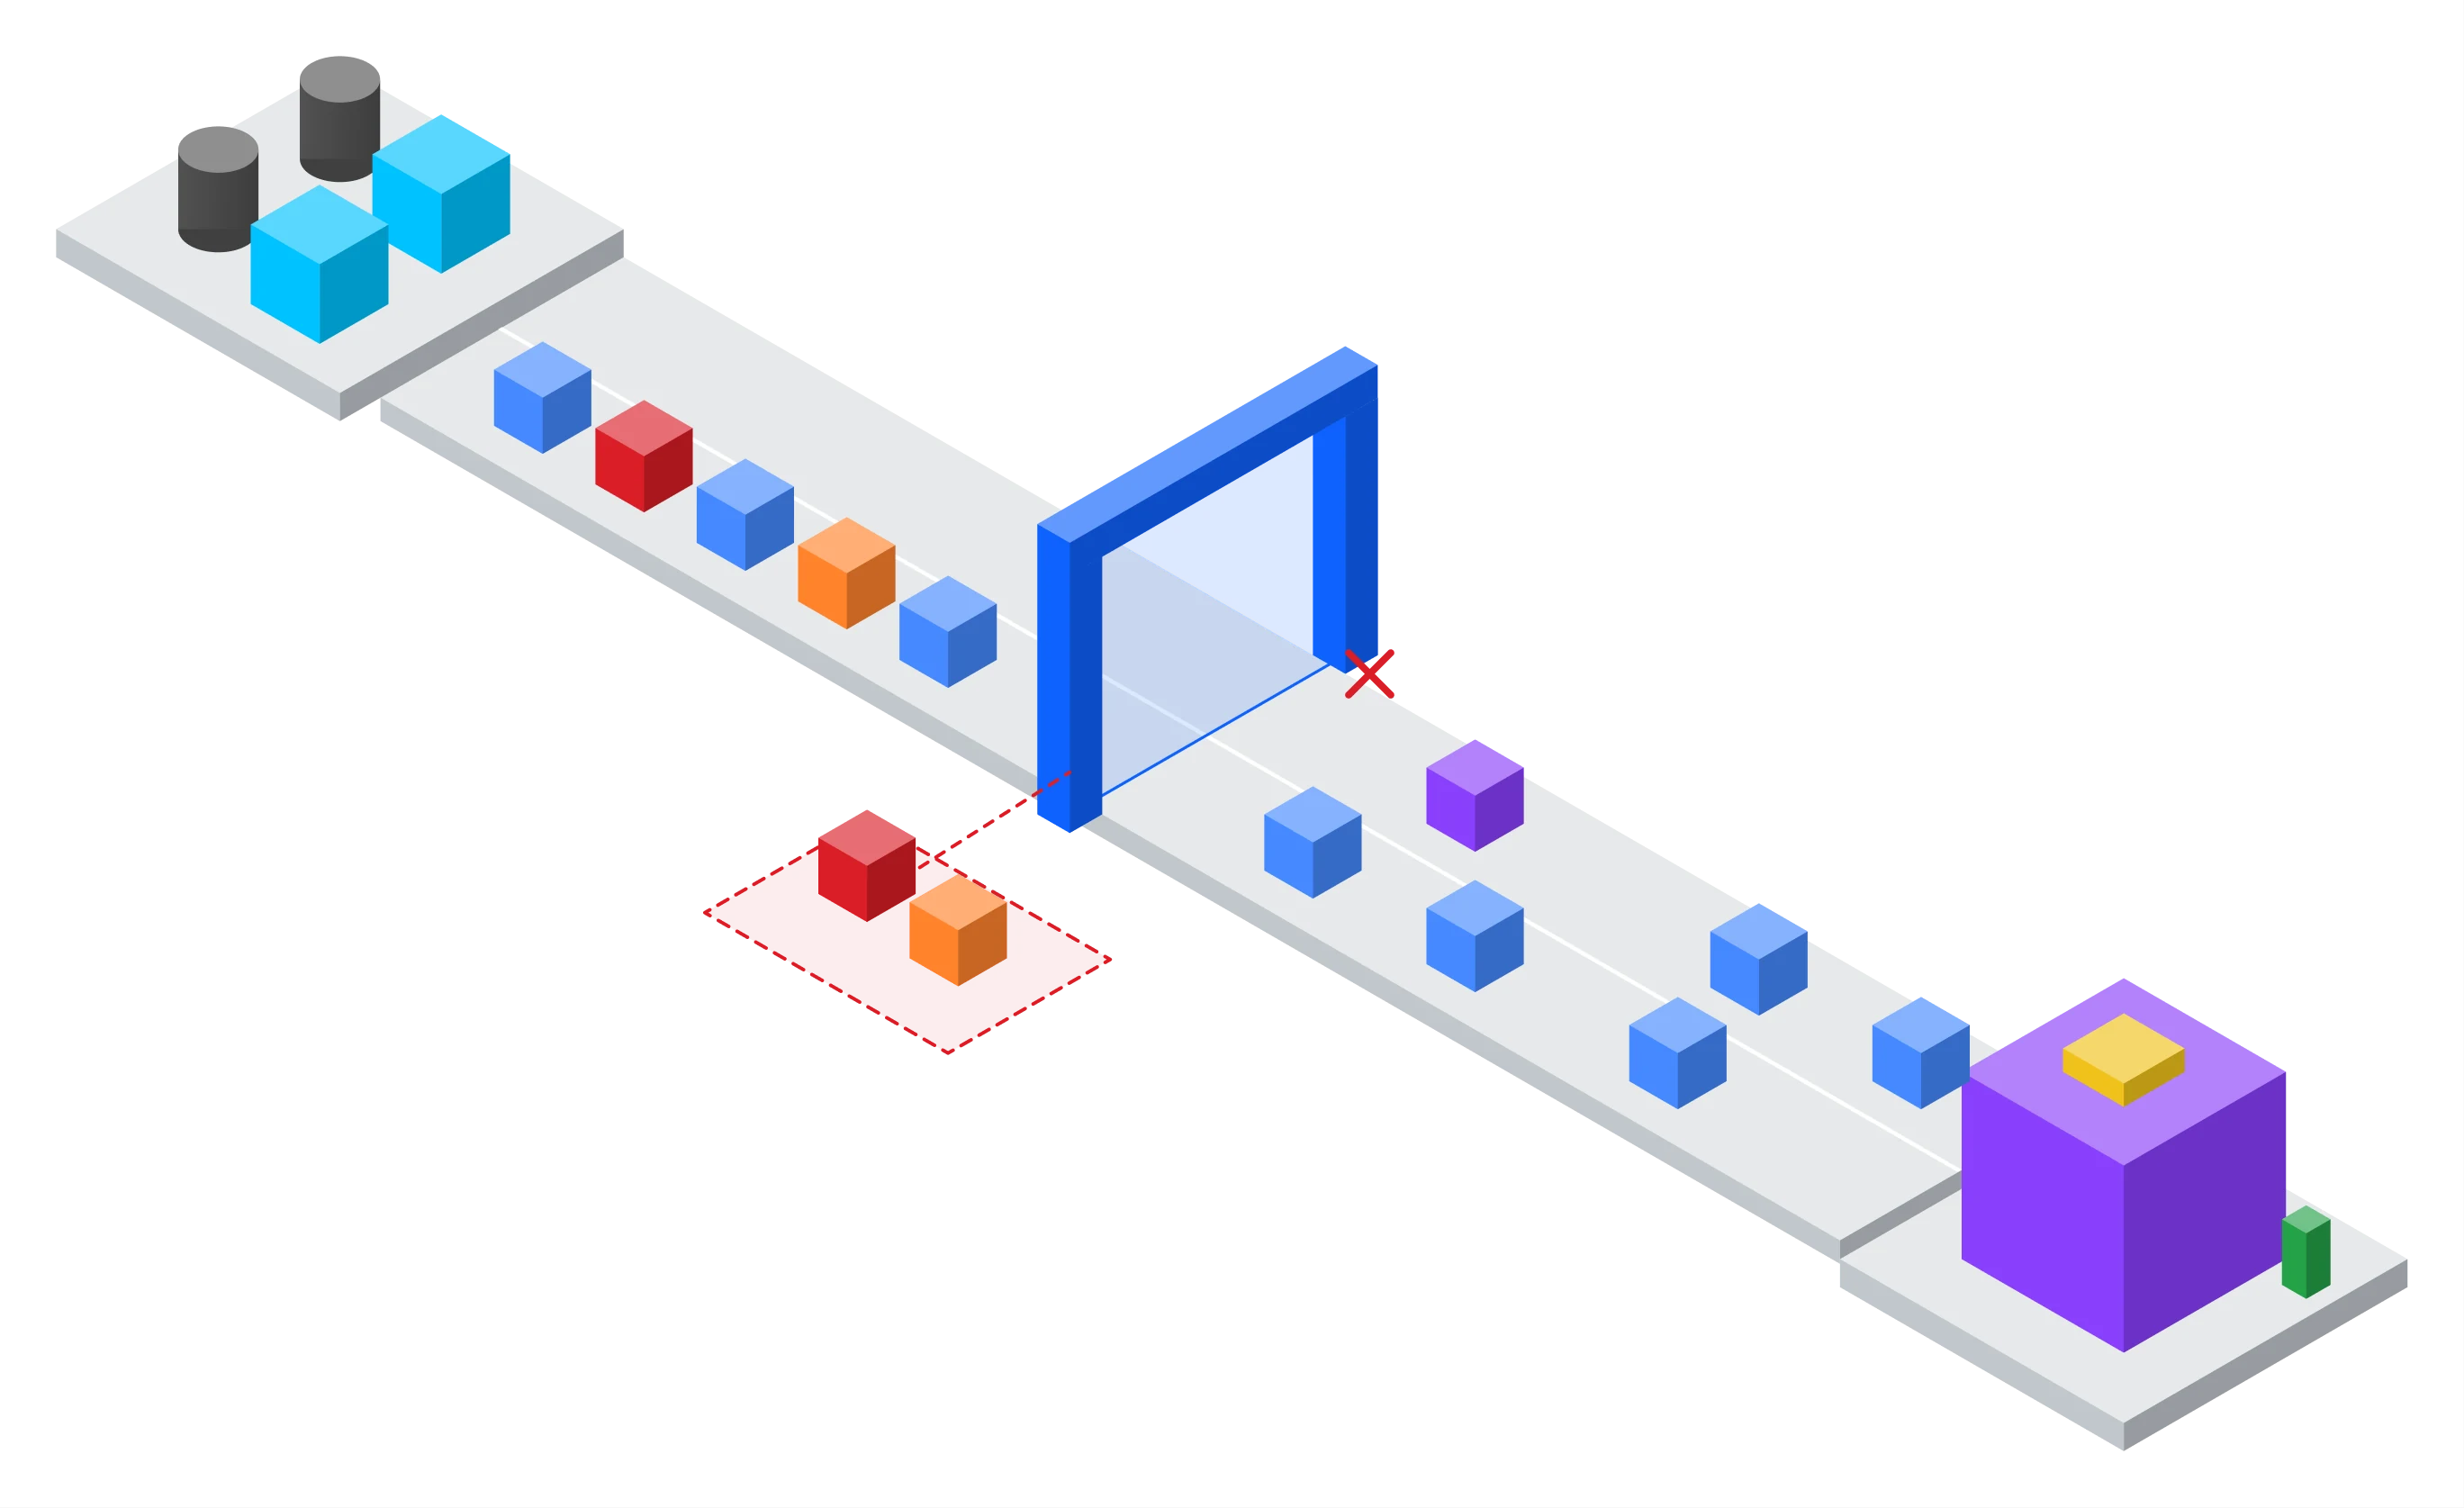
- Users and agentsPrompts, tool calls and API traffic heading for your AI.
- In-line gateEvery request inspected for intent, at the speed of the conversation.
- Set asidePrompt injection and jailbreak attempts never reach the model.
- Exfiltration stoppedSensitive data is held on the way out.
- AI keeps workingLegitimate work flows through without extra friction.
In-Line Prevention
Identify prompt injection, jailbreaks, data exfiltration and misuse of agent identities in line, going beyond what traditional guardrails can see.
Questions it helps you answer
- Can we stop a prompt injection before the model acts on it?
- Will security slow our AI down for real users?
- What stops sensitive data leaving through a model or an agent?
- Is every agent acting under an identity we recognise, with only the access it needs?
Pre-Emptive Assessment
Validate AI security, governance and compliance before production deployment, so every model and agent ships with evidence, not hope.
Questions it helps you answer
- Is this model or agent safe to ship?
- Can we show governance and compliance evidence before launch?
- What breaks when someone tries hard to misuse it?
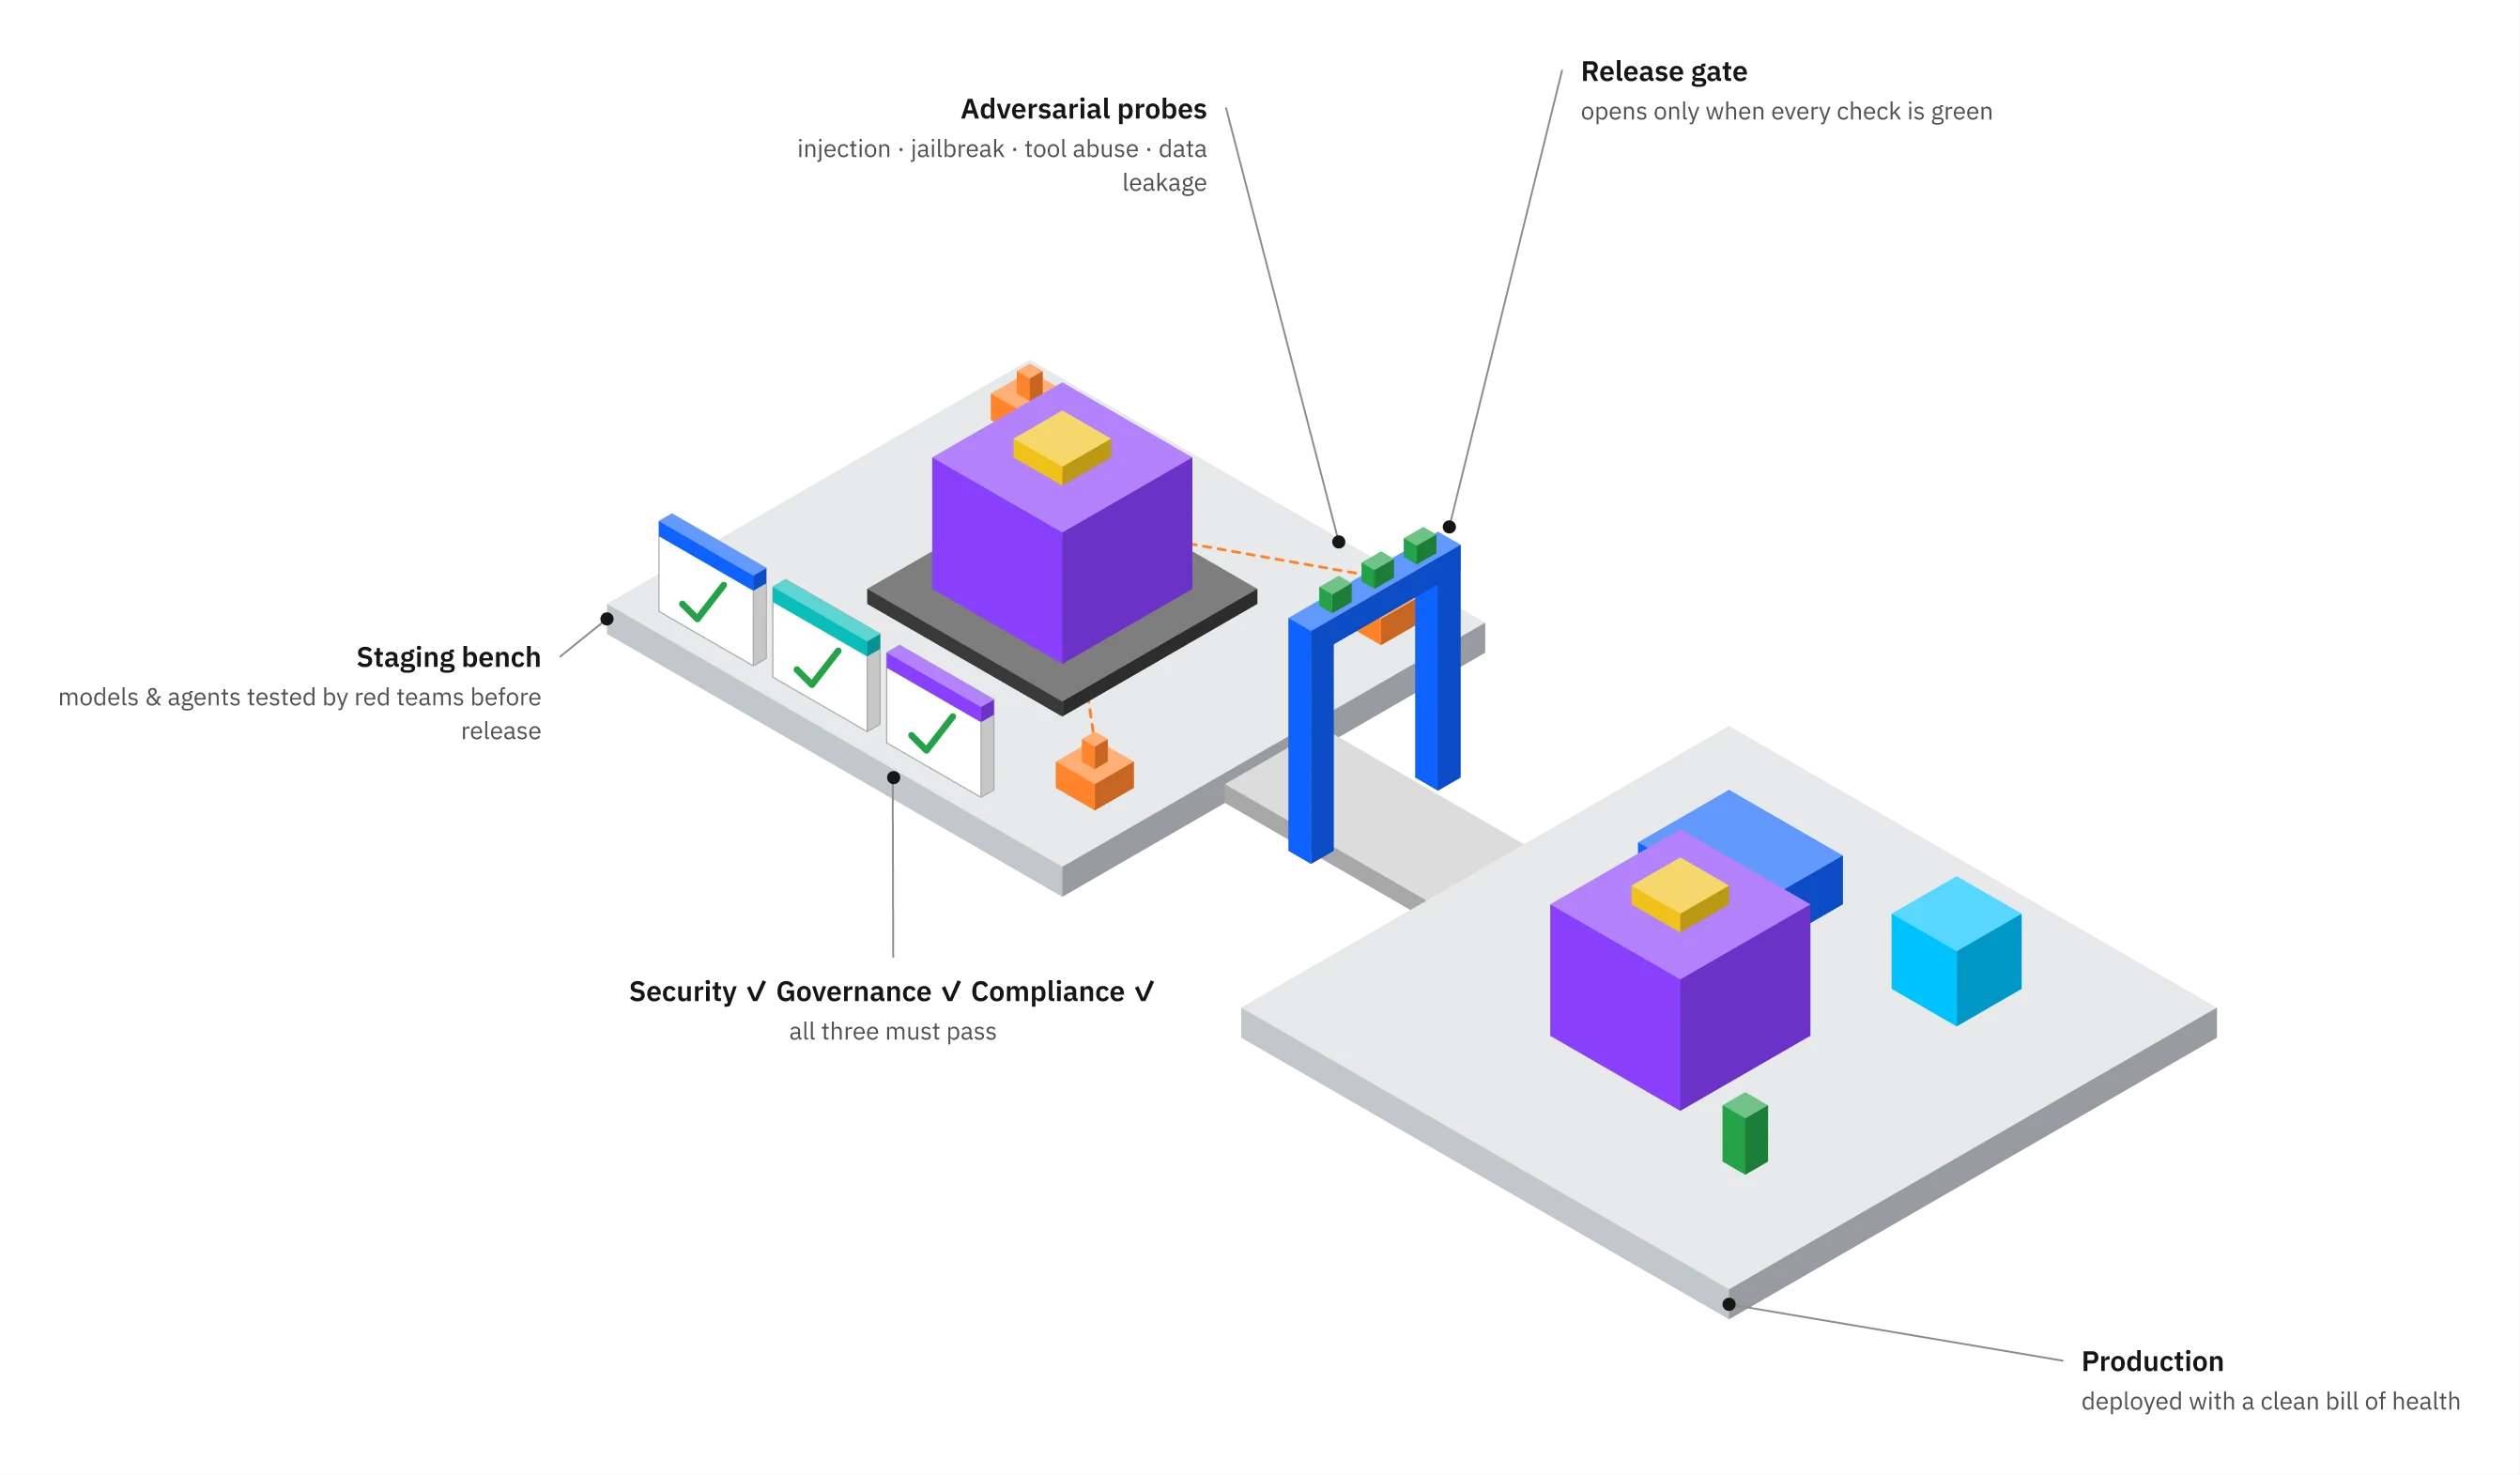
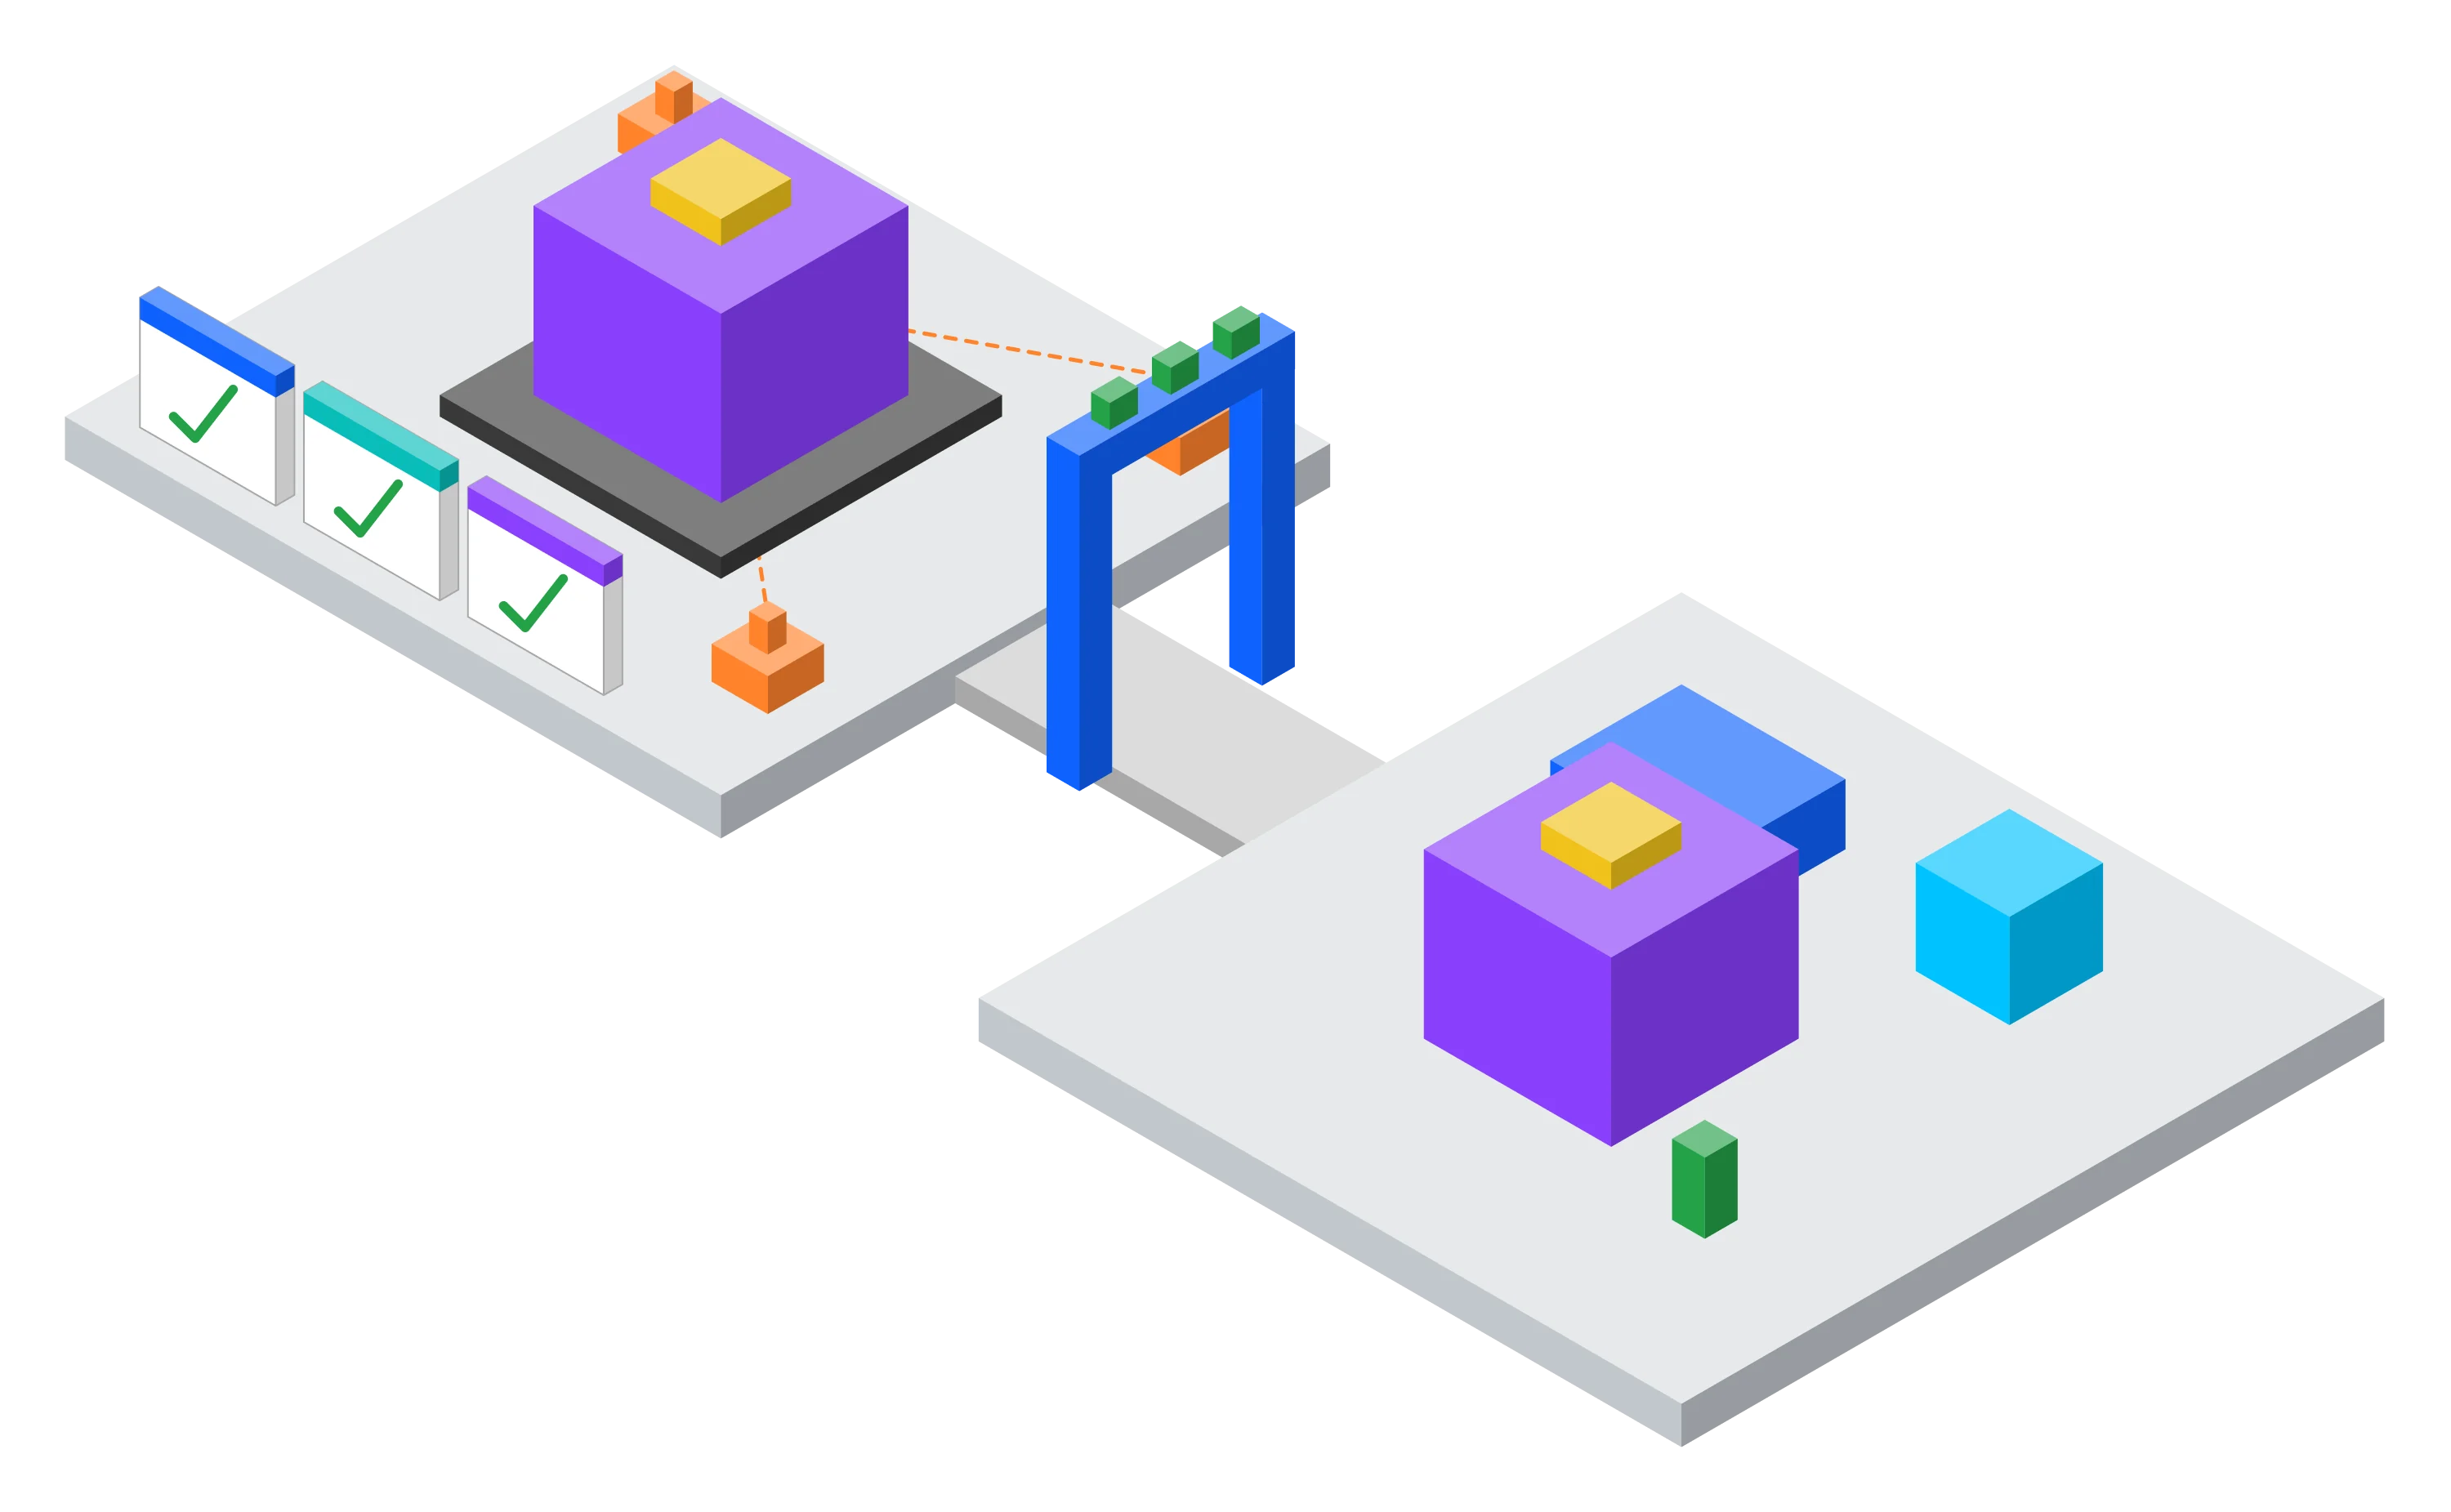
- StagingModels and agents are evaluated before release.
- Adversarial testingRealistic misuse attempts, run before attackers try them.
- Security, governance, complianceAll three checked, with evidence you can share.
- Release gateOpens when the checks pass.
- ProductionAI goes live with a clean bill of health.
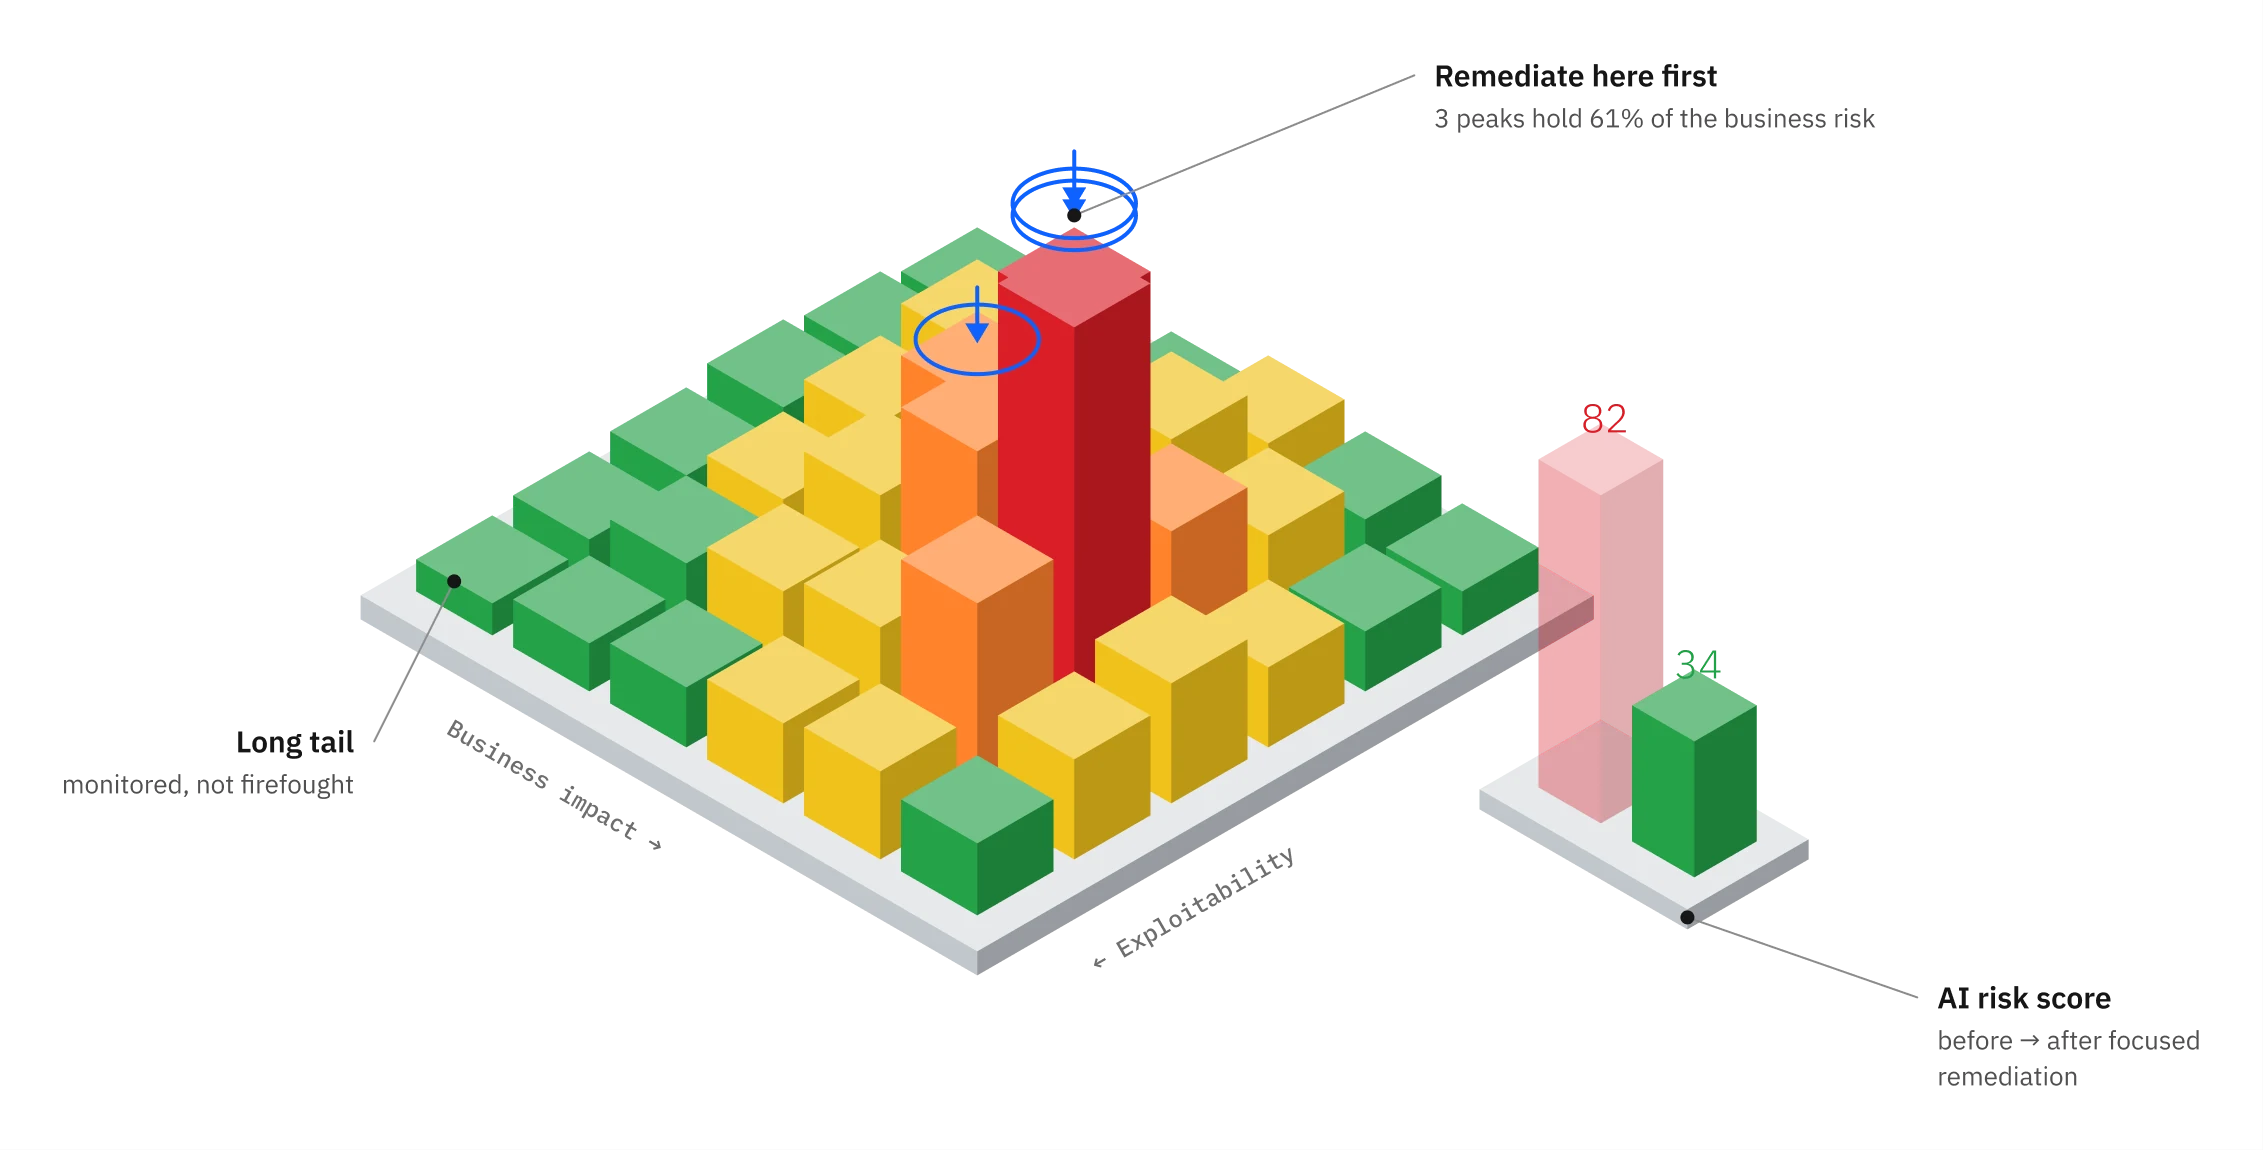
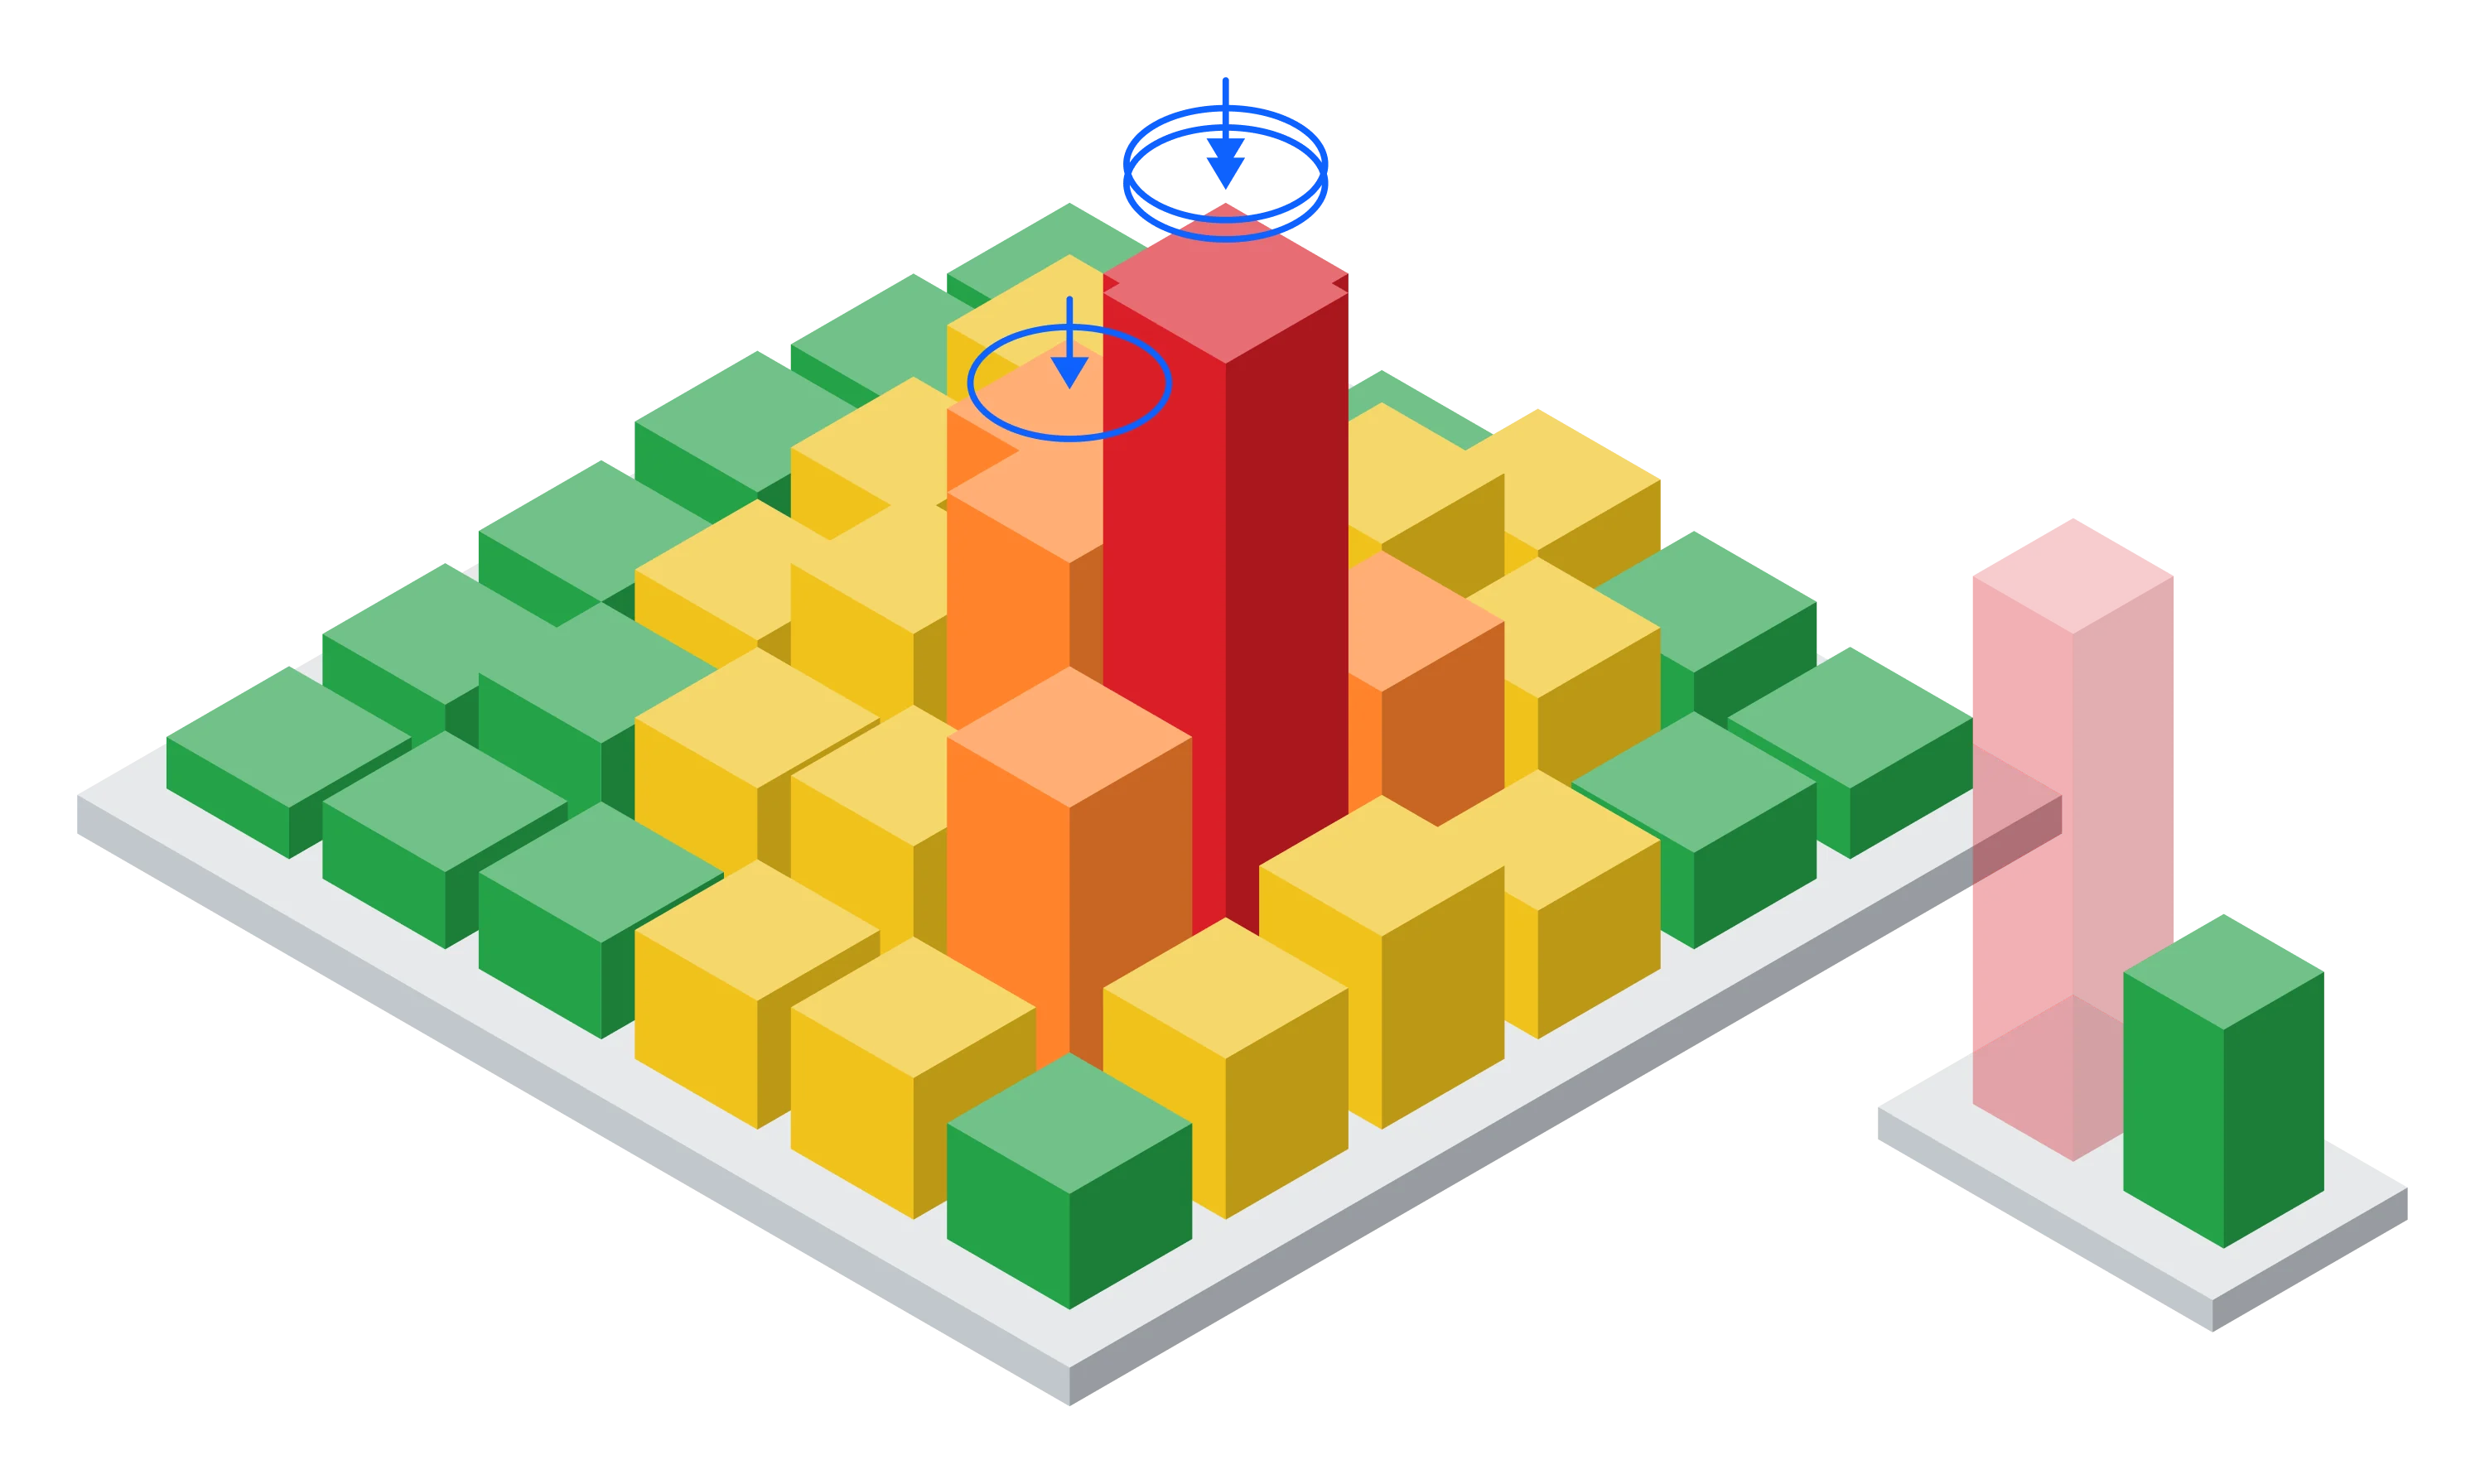
- The peaks that matterRisk ranked by business impact, so the first fix is the right fix.
- The long tailMonitored continuously, not firefought.
- Risk over timeSee whether remediation is actually bringing risk down.
Risk-Driven Optimization
I-THAM continuously quantifies AI risk, focusing remediation where it matters most to the business.
Questions it helps you answer
- Which AI risks matter most to our business right now?
- Where should our team spend its next hour?
- Is our AI risk going down over time?
AI-Native Response Orchestrator
Orchestrate real-time security response while maintaining business continuity. Every detection comes with a ready response: contain the threat, explain the intent behind it, keep a human in control of disruptive actions and record the evidence for audit.
Questions it helps you answer
- What happens in the first minutes after an AI incident?
- Who approves high impact actions?
- Can we contain a threat without taking the service down?
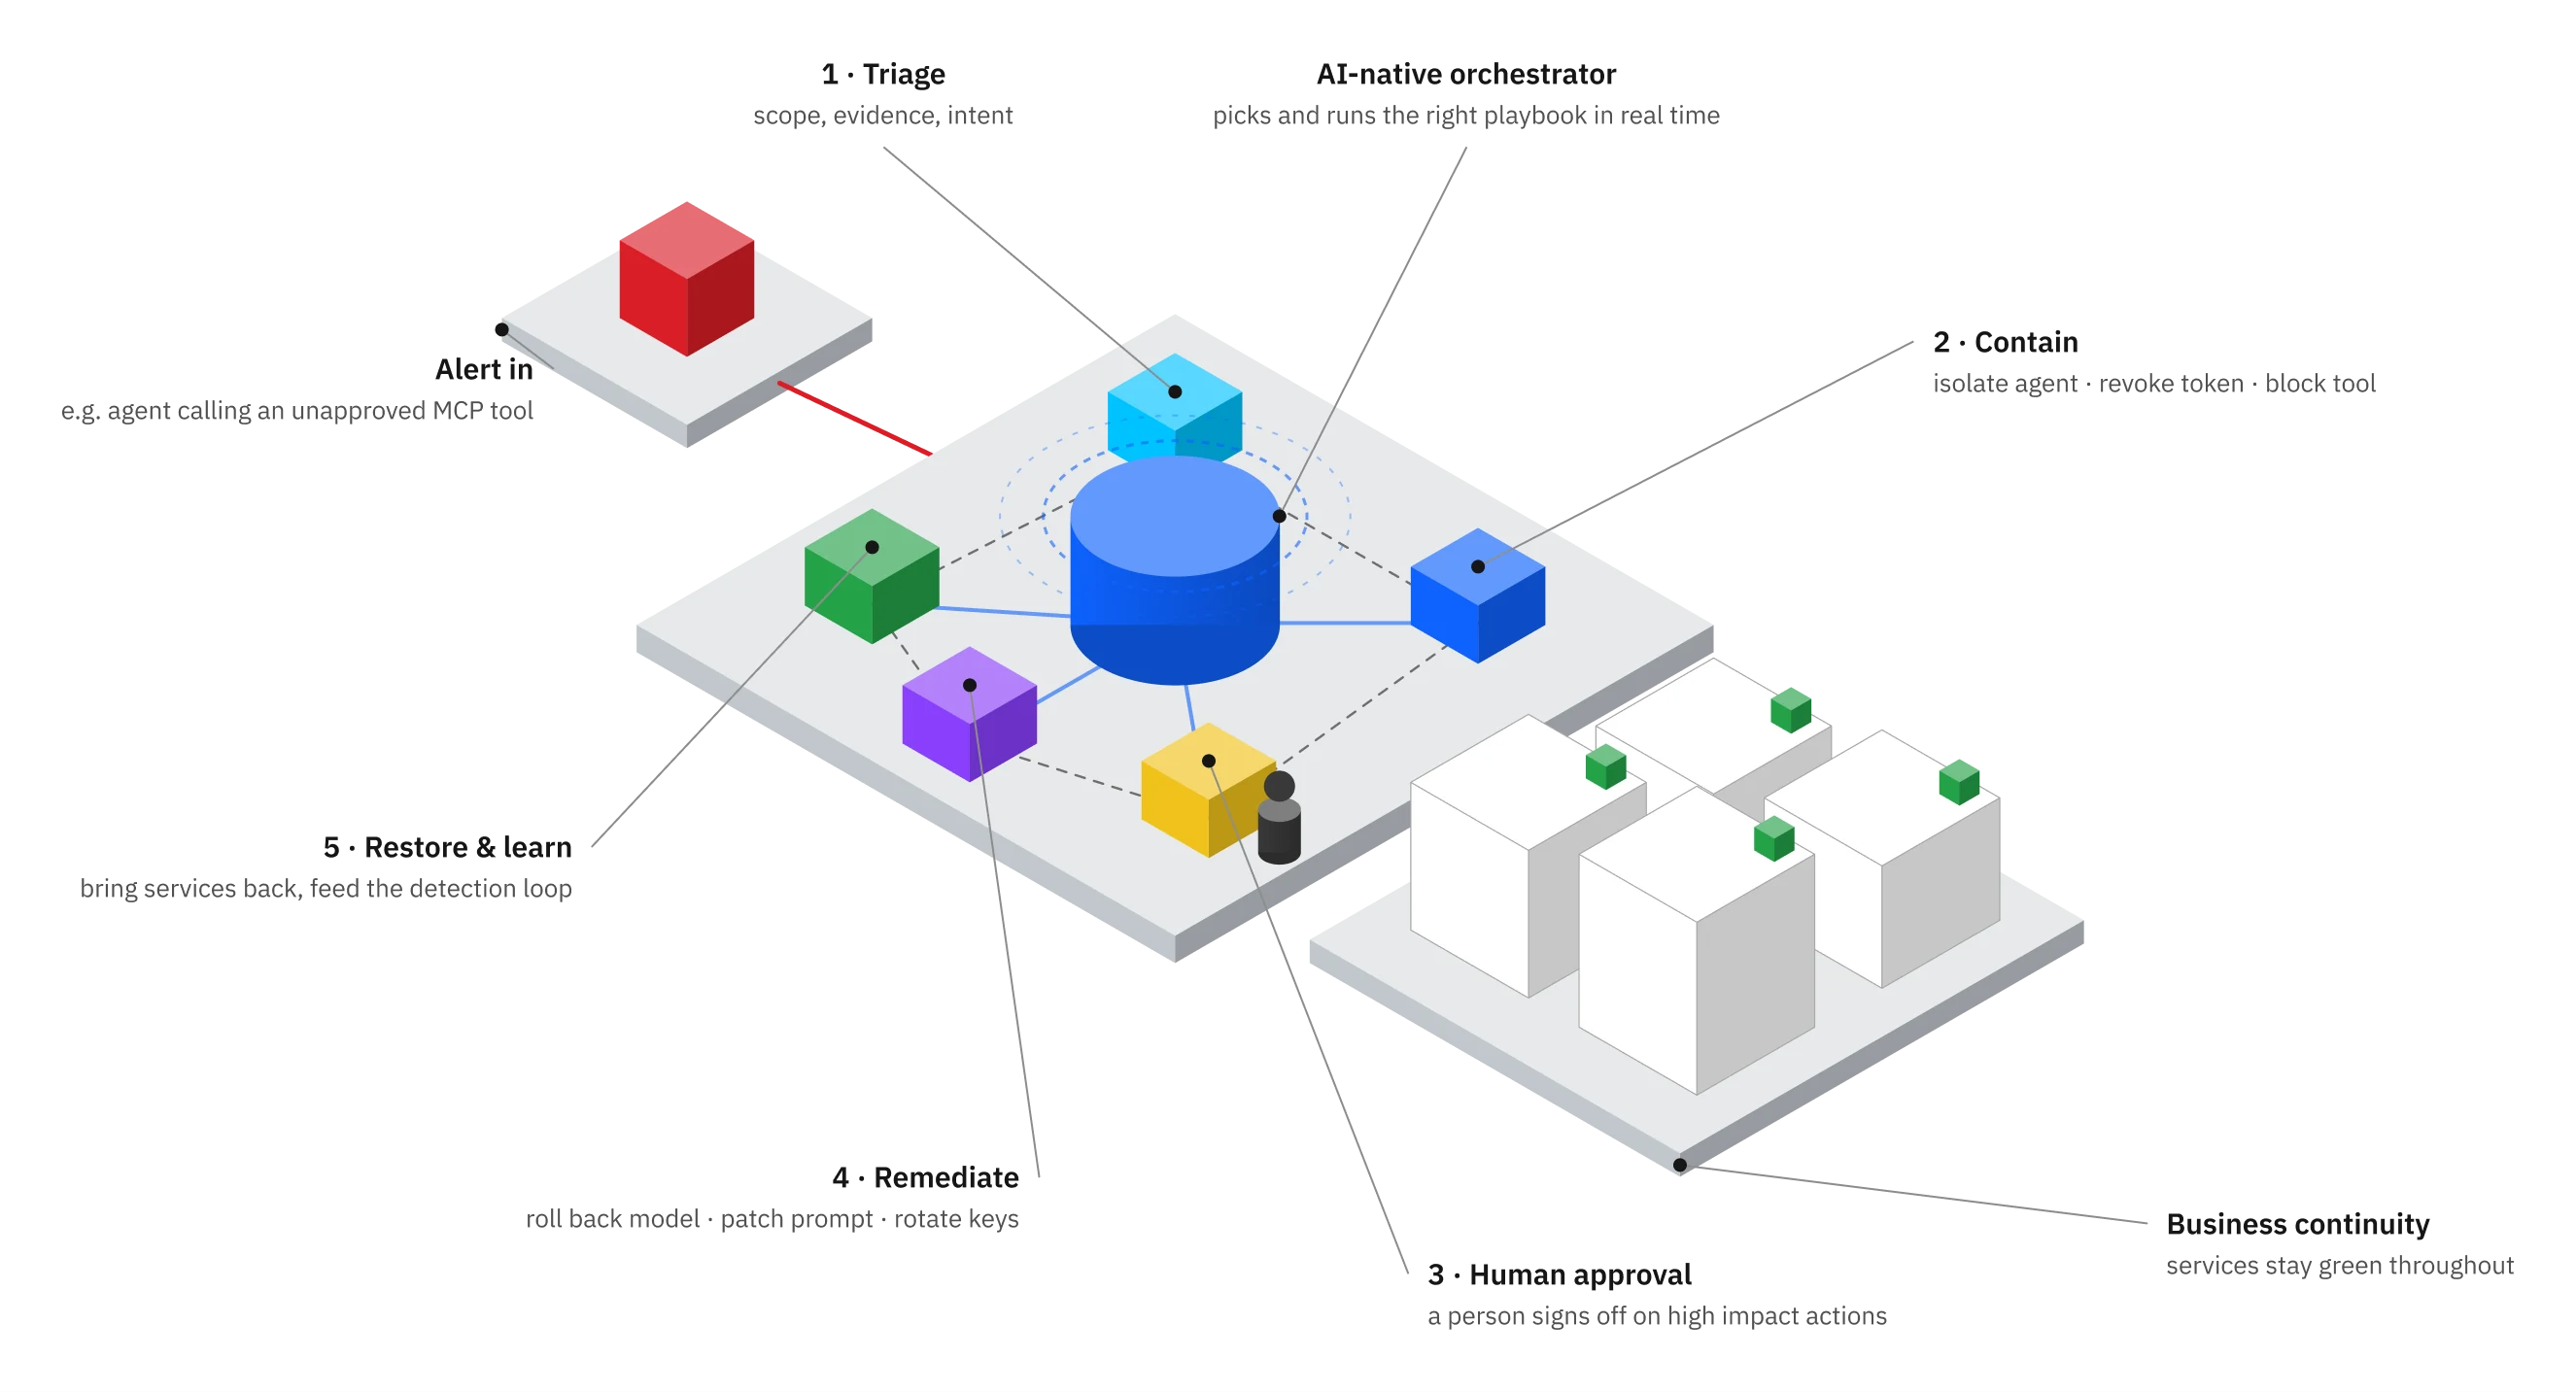
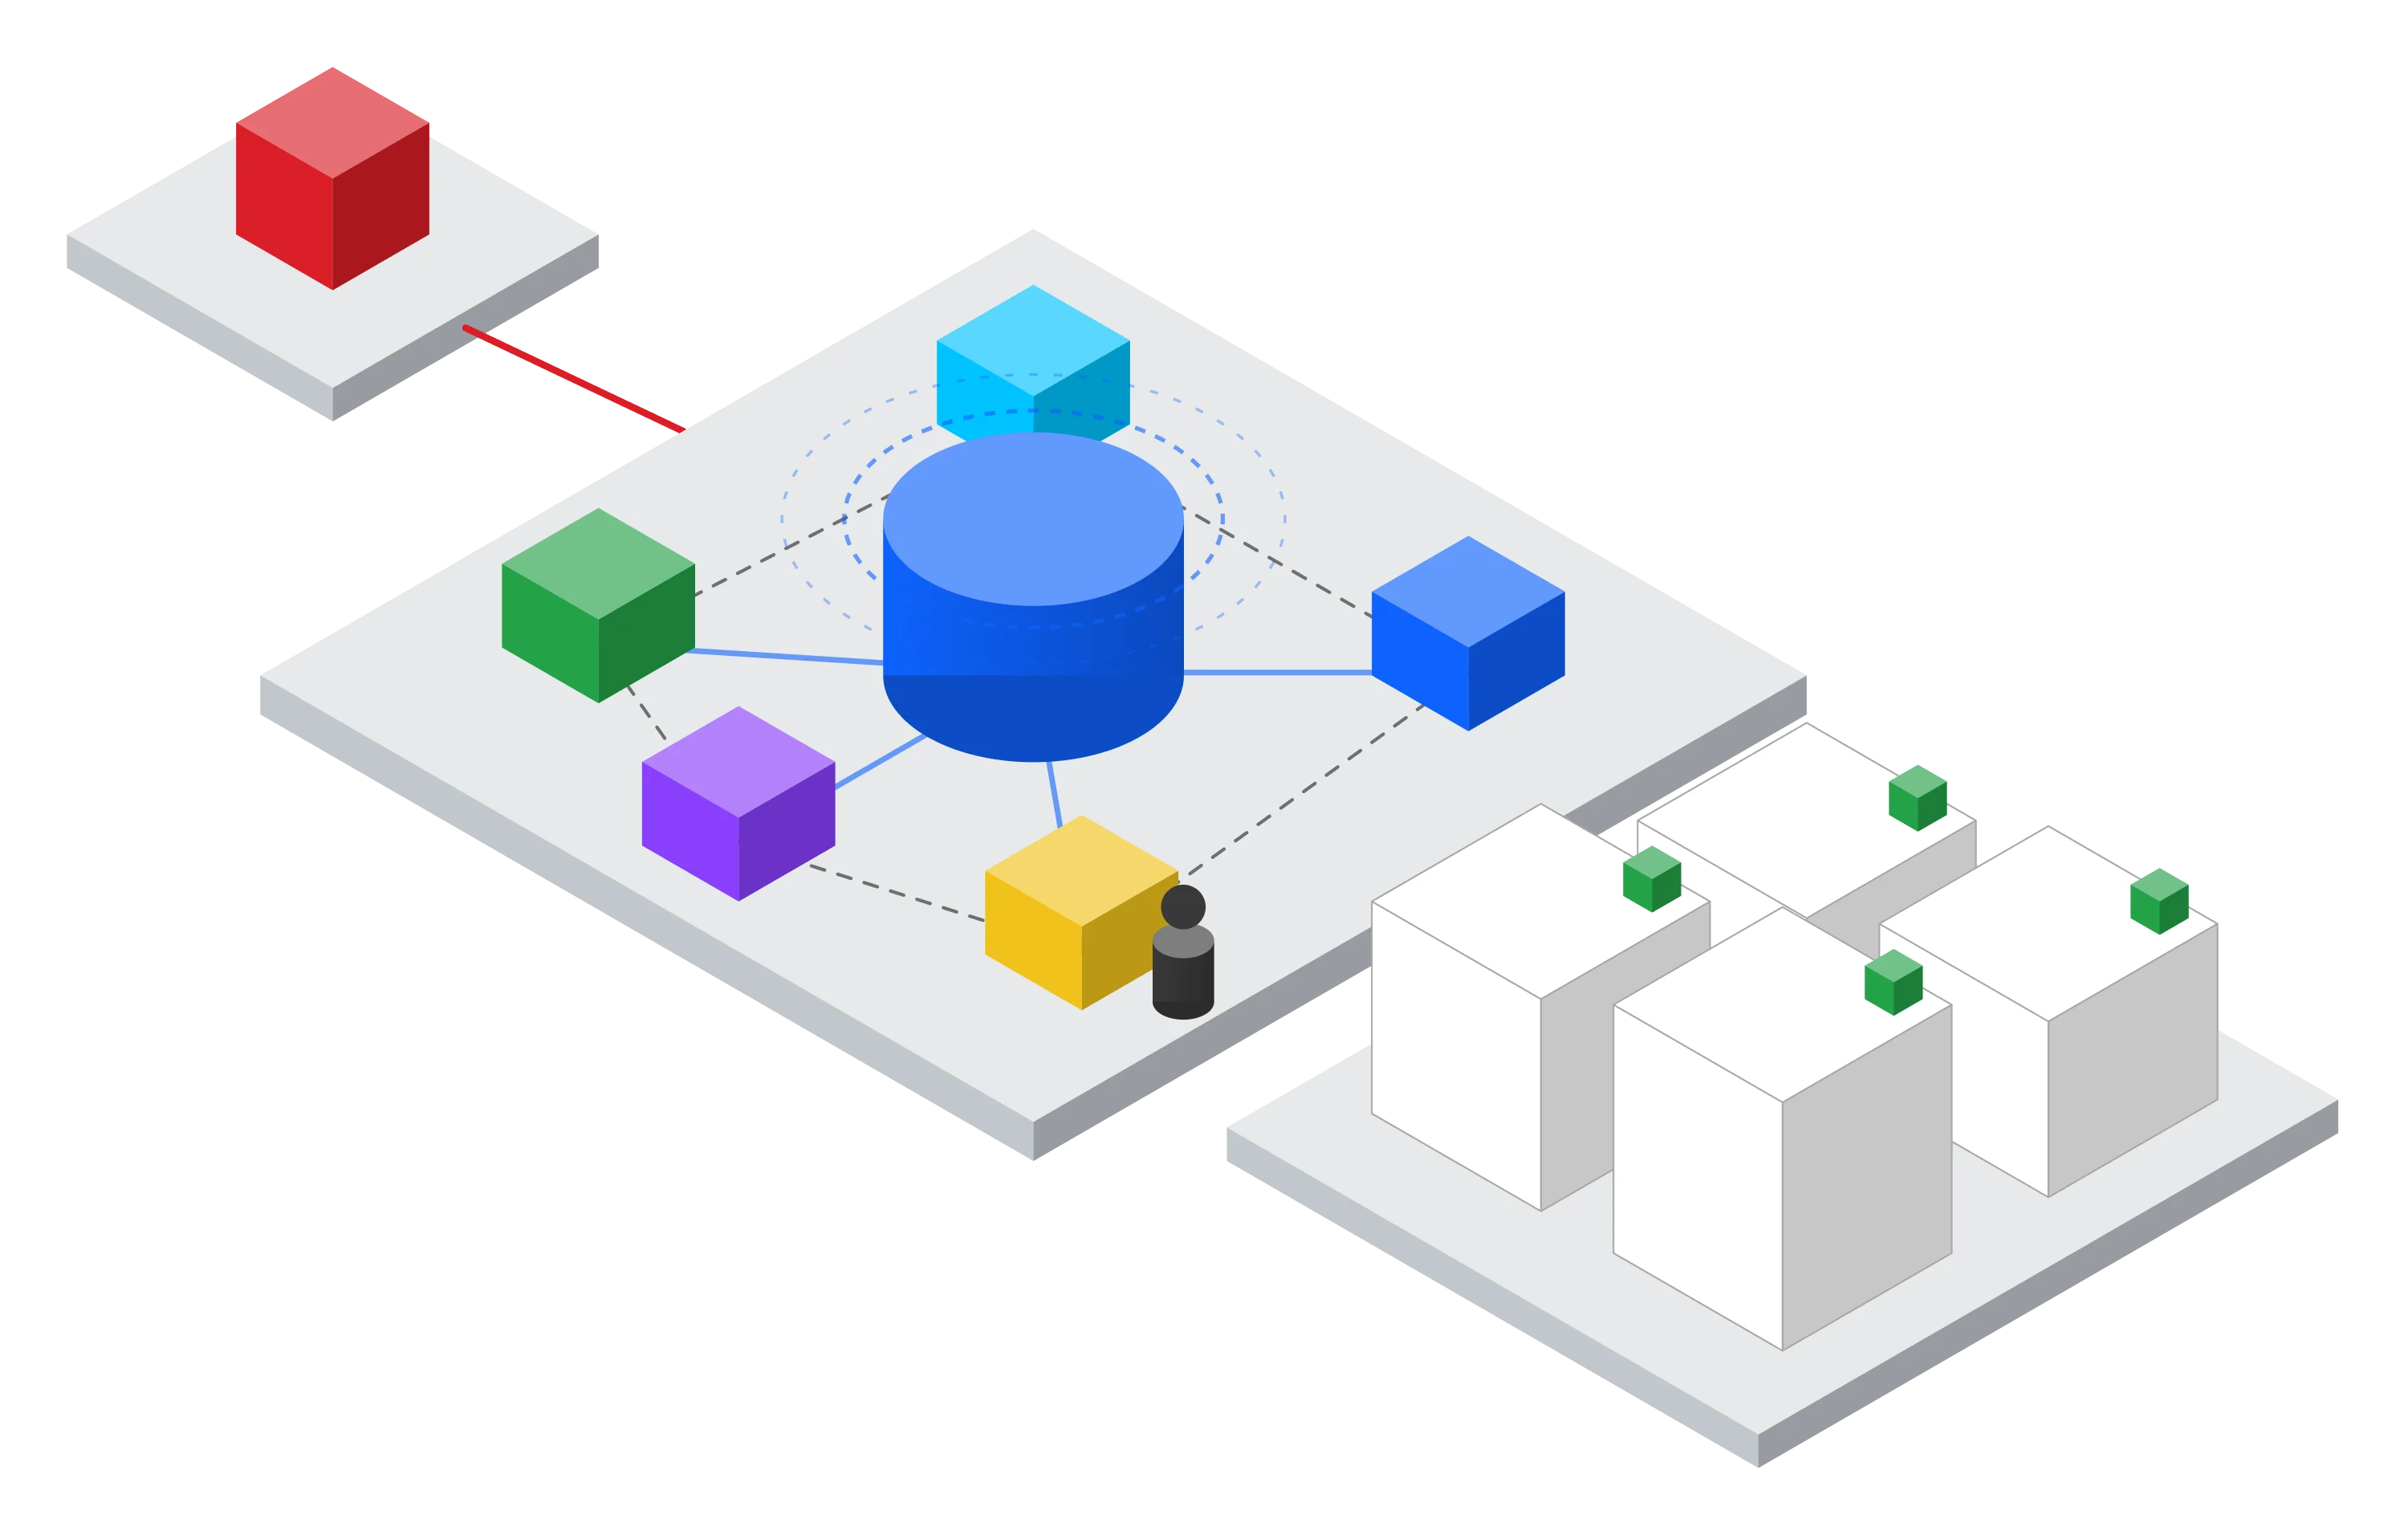
- AlertA signal comes in, for example an agent using a tool it should not.
- TriageScope, evidence and likely intent.
- ContainIsolate what is affected, quickly.
- Human approvalA person signs off on high impact steps.
- RemediateFix the cause, not only the symptom.
- Restore and learnBring services back and feed what was learned into detection.
- Business continuityServices stay up throughout.
Security for the whole AI lifecycle
Most tools protect one moment. I-THAM follows your AI from the first test to every decision it makes in production.
Know it is safe to ship
Pre-Emptive Assessment validates security, governance and compliance, so launching is a decision backed by evidence.
Stop what should never happen
Deep-Stream Detection sees novel attacks across the stack, including attempts to steal or tamper with your models, and In-Line Prevention stops injection, jailbreaks and exfiltration as they happen.
Improve, respond and prove it
Risk-Driven Optimization points effort at what matters, and the AI-Native Response Orchestrator handles incidents while the business keeps running.
About the platform
Where can we deploy I-THAM?
Wherever your AI runs. I-THAM is available as SaaS, in your private cloud, on premises and in fully air gapped environments.
How long does deployment take?
Less than 30 minutes, for every deployment option: SaaS, private cloud, on premises and fully air gapped.
What does I-THAM integrate with?
I-THAM integrates with leading security technologies and collaboration tools, and comes with its own MCP integration for the AI SOC.
Does I-THAM replace our existing security tools?
No. I-THAM is designed to work alongside the security stack you already run, adding protection that is built for how AI systems behave.
How does I-THAM protect agent and non-human identities?
In-Line Prevention recognises every AI agent and service identity and ties each tool and model call to the agent and the person behind it. Unknown agents, blocked identities and agents reaching beyond their permissions are stopped before they act, and misuse of agent credentials is flagged for response. Every decision is recorded, so it can be audited.
Can I-THAM help with AI governance and compliance?
Yes. Pre-Emptive Assessment validates security, governance and compliance before production, so teams can show evidence before an AI system goes live.
How do we get started?
Book a demo and we will walk through your AI stack and whether I-THAM is a good fit.